SonicWall SMA 1000 Series
Overview
SonicWall Secure Mobile Access 1000 Series logs are structured text-based records (mostly syslog-like and HTTP access formats, with XML exports) that capture timestamped system, administrative, access, tunnel, flow, web proxy, unregistered device, and WorkPlace events for monitoring, auditing, and incident analysis.
- Vendor: SonicWall
- Supported environment: On prem
- Version compatibility: 12.5
- Detection based on: Telemetry
- Supported application or feature: DNS records
Configure
This setup guide will show you how to forward your SonicWall SMA 1000 Series logs to Sekoia.io by means of a syslog transport channel.
Prerequisites
- Have an internal log concentrator (Rsyslog).
Enable Syslog forwarding for SonicWall SMA 1000 Series
- Log in the SonicWall SMA Appliance Management Console.
- Go to
Monitoring > Logging > Configure Logging. - In the
Services Log Levelsection, define the severity level of log messages. -
In the
Syslog Configurationsection, type the IP address and the port of your log concentrator as primary syslog server (Server #1).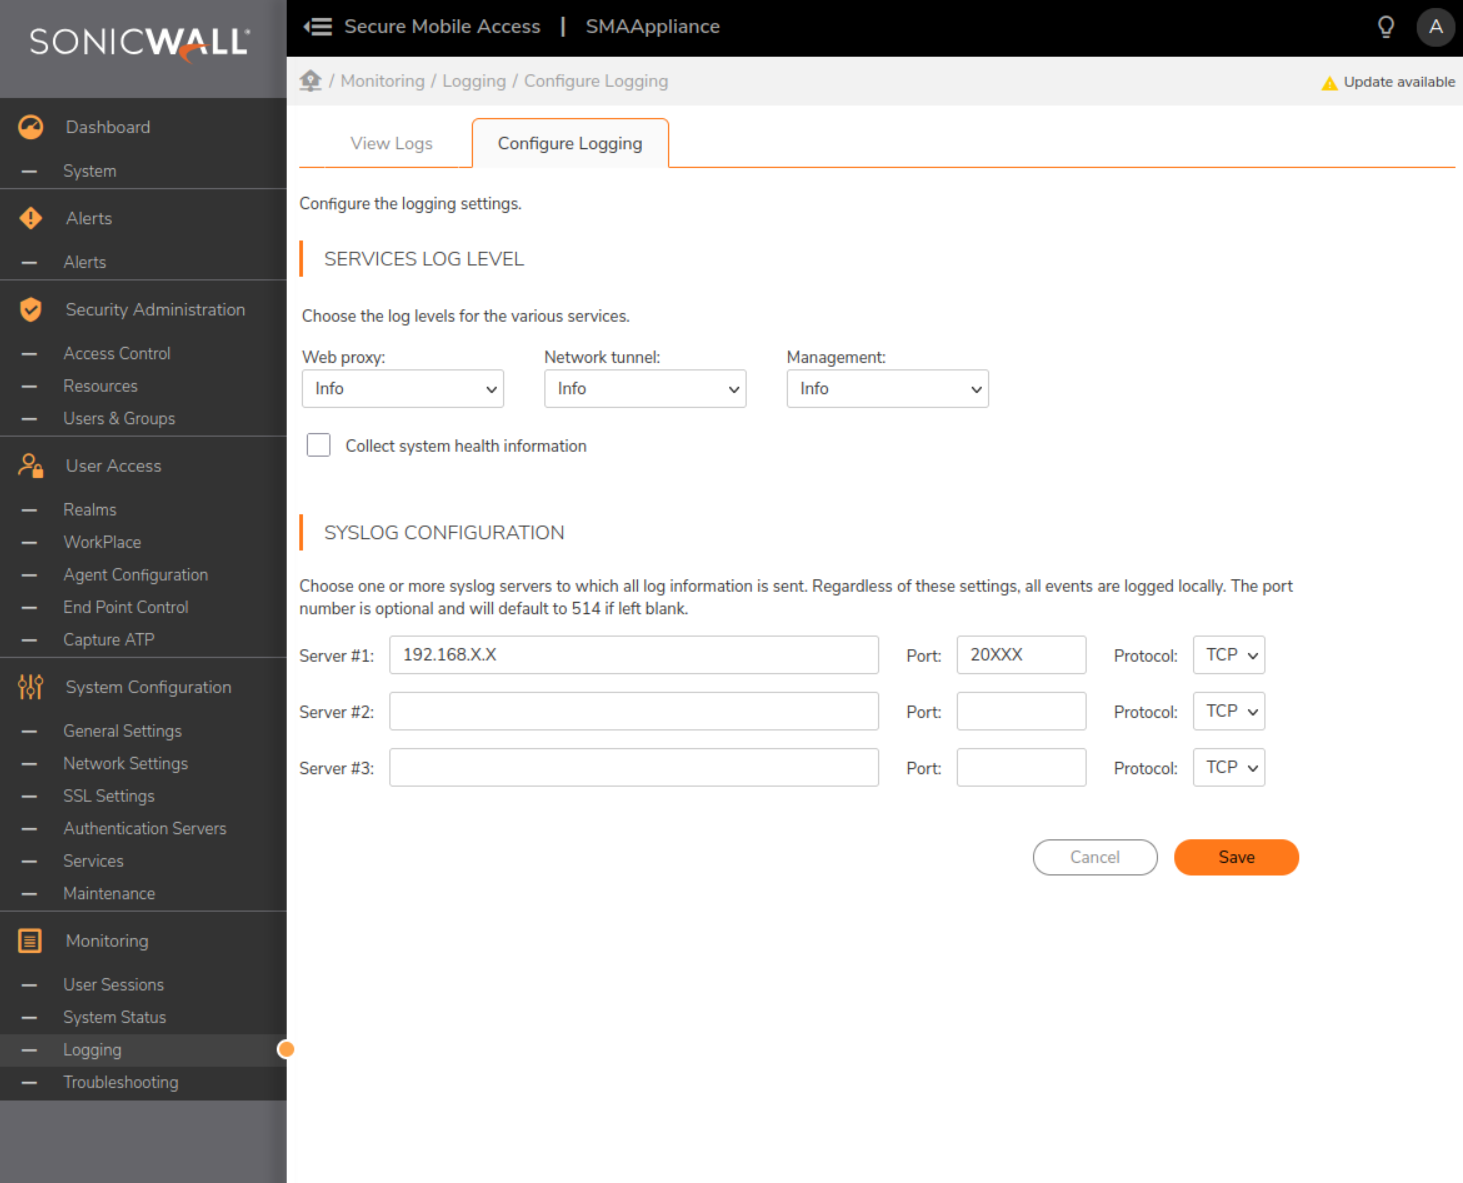
-
Click
Saveto save your logging settings.
Create the intake
Go to the intake page and create a new intake from the SonicWall SMA 1000 Series format.
Forward logs to Sekoia.io
Please consult the Syslog Forwarding documentation to forward these logs to Sekoia.io.
Raw Events Samples
In this section, you will find examples of raw logs as generated natively by the source. These examples are provided to help integrators understand the data format before ingestion into Sekoia.io. It is crucial for setting up the correct parsing stages and ensuring that all relevant information is captured.
127.0.0.1 - admin [25/Jul/2025:05:30:52 -0700] "GET /Console/PendingChanges HTTP/1.1" 200 308
198.51.100.10 - - [01/Jul/2026:15:53:26 +0000] "POST /j_security_check HTTP/1.1" 303 0
Info 6/3/2025 00:31:02 admin Applied configuration changes
2025-07-25T12:31:06+00:00 AMC@gateway01.example.com local4.info AMC: 2025-07-25 12:31:06 +0000 INFO com.aventail.mgmt.rest.console.centralmanagement.managed.sharedstate.TrafficOptimizerConfigurationResource12_2 - Clearing traffic optimizer configuration
2026-07-01 15:53:26 +0000 INFO [admin]: Login succeeded - Address=198.51.100.10
pam_unix(cron:session): session closed for user root
2026-07-02 14:33:15 +0000 INFO [admin]: Adding user group - Name=grp4
2026-07-02 14:48:12 +0000 ERROR com.aventail.mgmt.jetty.JettyServer - SSL handshake failed: Closed during handshake (198.51.100.10:40236)
2026-07-02 14:52:48 +0000 INFO [admin]: Added address pool - ID=ID1111111111111111 Name=Test Example
(root) CMD ( run-parts --report /etc/cron.hourly > /dev/null 2>&1)
[::ffff:198.51.100.10]:59234 - "(user02)@(CT)" "31/Jul/2025:14:41:23.073 +0530" 1.2 tunnel 203.0.113.20 -1 112639 137450 165 W"42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24"
198.51.100.10:59260 - "(user02)@(CT)" "31/Jul/2025:14:40:47.815 +0530" 1.2 flow:tcp 203.0.113.20:443 0 5436 129963 125 W"42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24"
[03/Sep/2026:11:04:57.514525 +0200] sma8200v-01.example.com 000000 kt 00000000 Info Audit Src='198.51.100.25:53083' User='(user.beta@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:TCP' Dest='203.0.113.175:7680' Error='0xffffffff' SrcBytes='52' DstBytes='0' Duration='0' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7890.' SessionKey='SMA8200v:6a992741:00000000'
EventMessage: Resource Access - User='(user.alpha@example.com)@(EXAMPLE_ORG)', Src='198.51.100.10:43496', Dest_IP='203.0.113.56:53', Rule Info='DEFAULT RULES', Full Destination='203.0.113.56:53', Access Agent='-', Allowed='1'
EventMessage: Resource Access - User='(user.beta@example.com)@(EXAMPLE_ORG)', Src='198.51.100.11:52532', Dest_IP='203.0.113.239:7680', Rule Info='-', Full Destination='host-a.internal.example.com:7680', Access Agent='-', Allowed='0'
EventMessage: Resource Access - User='(user.gamma@example.com)@(EXAMPLE_ORG)', Src='198.51.100.12:53210', Dest_IP='203.0.113.120:7680', Rule Info='TOULOUSE RULES', Full Destination='host-b.internal.example.com:7680', Access Agent='-', Allowed='1'
EventMessage: Resource Access - User='(user.delta@example.com)@(EXAMPLE_ORG)', Src='198.51.100.13:53211', Dest_IP='203.0.113.121:389', Rule Info='-', Full Destination='203.0.113.121:389', Access Agent='-', Allowed='0'
[03/Sep/2026:11:04:58.123456 +0200] sma8200v-02.example.com 000000 kt 00000000 Info Audit Src='198.51.100.30:54001' User='(user.gamma@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:TCP' Dest='203.0.113.88:443' Error='0' SrcBytes='1024' DstBytes='2048' Duration='9' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7891.' SessionKey='SMA8200v:6a992742:00000000'
[03/Sep/2026:11:04:59.654321 +0200] sma8200v-03.example.com 000000 kt 00000000 Info Audit Src='198.51.100.31:54002' User='(user.delta@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:UDP' Dest='203.0.113.89:5353' Error='0xffffff92' SrcBytes='512' DstBytes='256' Duration='3' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7892.' SessionKey='SMA8200v:6a992743:00000000'
[29/Jul/2025:14:02:38.051761 +0000] gateway-kernel-01.example.com 000000 kp 0000020a Internal Misc <KERNEL> created channel (pid=6268):0000000021ce9936
[6/3/2025 00:32:36.115] E-Class SMASSLVPN 002421 ps 100004b3 Info EWACL User ' (198.51.100.10 (user-example)@(group01)' connecting from '198.51.100.10:37975' matched rule 'accessRule(AV1091719670706:preauth access rule)', access to '127.0.0.1:455' is permitted.
[6/3/2025 00:32:36.115 +0000] E-Class SMASSLVPN 027186 uk 00000001 Verbose System ::API::FAKEA145dFYNZimCKNWHB7p2q2Y=::(user01)@(group01)::CLIENT:: Interrogation: Evaluation of OPSWATAV AV1128462569762A [NortonAV.dll,Symantec Corp.,Symantec Client Security,>=,9.x,,,,,FALSE] results: FALSE
[02/Jul/2025:18:47:29.113075 +0000] SMAnode 013581 ps 00000000 Info System Auth: CRL-CERT: Cert verification status = 0, err = 19, reason = 'self-signed certificate in certificate chain', subject='/C=US/ST=Washington/L=Seattle/O=SonicWall/OU=Engineering/CN=Untrusted CA'
https://gateway.internal.example.com:8443/UnregisteredDevices.xml
https://gateway.internal.example.com:8443/UnregisteredDevices.xml?lastLoginTime=2026-08-07T12:00:00Z&platform=Windows&realm=Students&username=user.test&exported=true&deviceCount=10&limit=100
198.51.100.10 - (user01)@(AD) [6/3/2025 00:32:36.115 +0000] "GET /workplace/access/home HTTP/1.1" 200 15424
2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:24 +0530 DEBUG - GOT: CredentialsManager[teamSessionId=FAKESESSIONID7QuQWL3BGdokQ==,teamcredentials={username=user01} ,credentials={}]
2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:23 +0530 DEBUG - PolicyClientSession: <authorize:exit> uri=http://127.0.0.1:8085/ctdownload/ status=PCL_STATUS_SUCCESS
2025-06-30T14:17:23+05:30 127.0.0.1/127.0.0.1 local7.debug DEBUG [22:03:03,617] pcsession: <authorize:exit> uri=smb://fileshare01.example.com/marketing status=SUCCESS
2025-06-30T14:17:23+05:30 127.0.0.1/127.0.0.1 local7.debug DEBUG [22:12:15,043] pcsession: <authorize:exit> uri=http://app.internal.example.com status=FAILURE
2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:23 +0530 DEBUG - PolicyClientSession: <authorize:exit> uri=http://127.0.0.1:8085/ctdownload/ status=PCL_STATUS_SUCCESa
Detection section
The following section provides information for those who wish to learn more about the detection capabilities enabled by collecting this intake. It includes details about the built-in rule catalog, event categories, and ECS fields extracted from raw events. This is essential for users aiming to create custom detection rules, perform hunting activities, or pivot in the events page.
Related Built-in Rules
The following Sekoia.io built-in rules match the intake SonicWall Secure Mobile Access 1000 Series. This documentation is updated automatically and is based solely on the fields used by the intake which are checked against our rules. This means that some rules will be listed but might not be relevant with the intake.
SEKOIA.IO x SonicWall Secure Mobile Access 1000 Series on ATT&CK Navigator
Active Directory Data Export Using Csvde
Detects the use of Csvde, a command-line tool from Windows Server that can be used to export Active Directory data to CSV files. This export doesn't include password hashes, but can be used as a discovery tool to enumerate users, machines and group memberships.
- Effort: elementary
AdFind Usage
Detects the usage of the AdFind tool. AdFind.exe is a free tool that extracts information from Active Directory. Wizard Spider (Bazar, TrickBot, Ryuk), FIN6 and MAZE operators have used AdFind.exe to collect information about Active Directory organizational units and trust objects
- Effort: elementary
Adexplorer Usage
Detects the usage of Adexplorer, a legitimate tool from the Sysinternals suite that could be abused by attackers as it can saves snapshots of the Active Directory Database.
- Effort: advanced
Advanced IP Scanner
Detects the use of Advanced IP Scanner. Seems to be a popular tool for ransomware groups.
- Effort: master
Bloodhound and Sharphound Tools Usage
Detects default process names and default command line parameters used by Bloodhound and Sharphound tools.
- Effort: intermediate
Burp Suite Tool Detected
Burp Suite is a cybersecurity tool. When used as a proxy service, its purpose is to intercept packets and modify them to send them to the server. Burp Collaborator is a network service that Burp Suite uses to help discover many kinds of vulnerabilities (vulnerabilities scanner).
- Effort: intermediate
CVE-2018-11776 Apache Struts2
Apache Struts versions 2.3 to 2.3.34 and 2.5 to 2.5.16 suffer from possible Remote Code Execution when alwaysSelectFullNamespace is true (either by user or a plugin like Convention Plugin) and then: results are used with no namespace and in same time, its upper package have no or wildcard namespace and similar to results, same possibility when using url tag which doesn't have value and action set and in same time, its upper package have no or wildcard namespace.
- Effort: intermediate
CVE-2018-13379 Fortinet Exploit
Detects the successful exploitation of the Fortinet FortiOS CVE-2018-13379. This CVE is one of the most exploited CVEs since 2018. It is exploited by APT threat actors as well as cybercriminals. The exploitation of this CVE lead an unauthenticated user to get full access to FortiOS system file through SSL VPN via specially crafted HTTP resource requests. The exploit read /dev/cmdb/sslvpn_websession file, that contains login and passwords in (clear/text). An HTTP response status code = 200, means the file was successfully accessed. This vulnerability affects FortiOS 5.6.3 to 5.6.7 and FortiOS 6.0.0 to 6.0.4.
- Effort: advanced
CVE-2019-0604 SharePoint
Detects the exploitation of the SharePoint vulnerability (CVE-2019-0604).
- Effort: advanced
CVE-2019-11510 Pulse Secure Exploit
Detects the successful exploitation of the Pulse Secure vulnerability CVE-2019-11510. This CVE is one of the most exploited CVEs since 2019. It is exploited by diverse threat actors, leading sometimes in ransomware deployement among these groups: Maze, Conti, Egregor, DoppelPaymer, NetWalker and REvil. But also APT actors such as APT29. The exploitation of this CVE allows a remote, unauthenticated attacker to compromise a vulnerable VPN server. The attacker may be able to gain access to all active users and their plain-text credentials. It may also be possible for the attacker to execute arbitrary commands on each VPN client as it successfully connects to the VPN server. The exploit reads /etc/passwd file to get access to login and passwords in (clear/text). An HTTP response status code = 200, means the file was successfully accessed. This vulnerability affects 8.1R15.1, 8.2 before 8.2R12.1, 8.3 before 8.3R7.1, and 9.0 before 9.0R3.4 products.
- Effort: elementary
CVE-2019-19781 Citrix NetScaler (ADC)
Detects CVE-2019-19781 exploitation attempt against Citrix NetScaler (ADC), Application Delivery Controller and Citrix Gateway Attack.
- Effort: elementary
CVE-2019-2725 Oracle Weblogic Exploit
Detects the successful exploitation of a deserialization vulnerability in Oracle Weblogic Server, CVE-2019-2725. This vulnerability affects versions 10.X and 12.1.3 of WebLogic that have the components wls9_async_response.war and wls-wsat.war enabled. It is a remote code execution which can be exploited without authentication via HTTP. An HTTP response status code = 202, means the target is vulnerable, the analyst then has to look in depth to check if a webshell has been uploaded or something else has been done.
- Effort: elementary
CVE-2020-0688 Microsoft Exchange Server Exploit
Detects the exploitation of CVE-2020-0688. The POC exploit a .NET serialization vulnerability in the Exchange Control Panel (ECP) web page. The vulnerability is due to Microsoft Exchange Server not randomizing the keys on a per-installation basis resulting in them using the same validationKey and decryptionKey values. With knowledge of these, values an attacker can craft a special viewstate to use an OS command to be executed by NT_AUTHORITY\SYSTEM using .NET deserialization. To exploit this vulnerability, an attacker needs to leverage the credentials of an account it had already compromised to authenticate to OWA.
- Effort: elementary
CVE-2020-1147 SharePoint
Detection of SharePoint vulnerability CVE-2020-1147.
- Effort: advanced
CVE-2020-14882 Oracle WebLogic Server
Detects the exploitation of the Oracle WebLogic Server vulnerability (CVE-2020-16952).
- Effort: advanced
CVE-2020-17530 Apache Struts RCE
Detects the exploitation of the Apache Struts RCE vulnerability (CVE-2020-17530).
- Effort: intermediate
CVE-2020-5902 F5 BIG-IP Exploitation Attempts
Detects the exploitation attempt of the vulnerability found in F5 BIG-IP and described in CVE-2020-5902.
- Effort: elementary
CVE-2021-20021 SonicWall Unauthenticated Administrator Access
Detects the exploitation of SonicWall Unauthenticated Admin Access.
- Effort: advanced
CVE-2021-20023 SonicWall Arbitrary File Read
Detects Arbitrary File Read, which can be used with other vulnerabilities as a mean to obtain outputs generated by attackers, or sensitive data.
- Effort: advanced
CVE-2021-21972 VMware vCenter
The vSphere Client (HTML5) contains a remote code execution vulnerability in a vCenter Server plugin. A malicious actor with network access to port 443 may exploit this issue to execute commands with unrestricted privileges on the underlying operating system that hosts vCenter Server. This affects VMware vCenter Server (7.x before 7.0 U1c, 6.7 before 6.7 U3l and 6.5 before 6.5 U3n) and VMware Cloud Foundation (4.x before 4.2 and 3.x before 3.10.1.2). POST request on the following PATH "/ui/vropspluginui/rest/services/uploadova". If in response body (500) the words it has "uploadFile", that means the vCenter is available to accept files via POST without any restrictions.
- Effort: intermediate
CVE-2021-21985 VMware vCenter
The VMware vSphere Client (HTML5) contains a remote code execution vulnerability due to lack of input validation in the Virtual SAN Health Check plug-in which is enabled by default in vCenter Server. A malicious actor with network access to port 443 may exploit this issue to execute commands with unrestricted privileges on the underlying operating system that hosts vCenter Server. This affects VMware vCenter Server (7.0 before 7.0 U2b, 6.7 before 6.7 U3n and 6.5 before 6.5 U3p) and VMware Cloud Foundation (4.x before 4.2.1 and 3.x before 3.10.2.1).
- Effort: advanced
CVE-2021-22123 Fortinet FortiWeb OS Command Injection
Detects Fortinet FortiWeb OS Command Injection (August 2021) vulnerability exploitation attempt. A remote, authenticated attacker can execute arbitrary commands on the system hosting a vulnerable FortiWeb WAF by sending a POST request with the command in the name field. At the time of writing this rule, it would appear that the request would respond in code 500 for a successful exploitation attempt.
- Effort: advanced
CVE-2021-22893 Pulse Connect Secure RCE Vulnerability
Detects potential exploitation of the authentication by-pass vulnerability that can allow an unauthenticated user to perform remote arbitrary file execution on the Pulse Connect Secure gateway. It is highly recommended to apply the Pulse Secure mitigations and seach for indicators of compromise on affected servers if you are in doubt over the integrity of your Pulse Connect Secure product.
- Effort: intermediate
CVE-2021-26855 Exchange SSRF
Detects the exploitation of ProyxLogon vulerability on Exchange servers.
- Effort: advanced
CVE-2021-34473 ProxyShell Attempt
Detects CVE-2021-34473 ProxyShell attempt against Microsoft Exchange Server, Remote Code Execution Vulnerability.
- Effort: advanced
CVE-2021-41773 Apache 2.4.49 Path Traversal
Detects successful exploitation of the Apache Path Traversal CVE-2021-41773.
- Effort: advanced
CVE-2021-43798 Grafana Directory Traversal
Grafana version 8.x has a 0day arbitrary file read (with no fix yet) based on a directory traversal vulnerability
- Effort: intermediate
Certificate Authority Modification
Installation of new certificate(s) in the Certificate Authority can be used to trick user when spoofing website or to add trusted destinations.
- Effort: master
Certify Or Certipy
Detects the use of certify and certipy which are two different tools used to enumerate and abuse Active Directory Certificate Services.
- Effort: advanced
Cobalt Strike Default Beacons Names
Detects the default names of Cobalt Strike beacons / payloads.
- Effort: intermediate
Cobalt Strike HTTP Default GET beaconing
Detects GET HTTP queries from known Cobalt Strike beacons (source code 4.3)
- Effort: advanced
Cobalt Strike HTTP Default POST Beaconing
Detects POST HTTP queries from known Cobalt Strike beacons (source code 4.3)
- Effort: advanced
Cryptomining
Detection of domain names potentially related to cryptomining activities.
- Effort: master
DNS Query For Iplookup
Detects dns query of observables tagged as iplookup.
- Effort: master
Detect requests to Konni C2 servers
This rule detects requests to Konni C2 servers. These patterns come from an analysis done in 2022, September.
- Effort: elementary
Discord Suspicious Download
Discord is a messaging application. It allows users to create their own communities to share messages and attachments. Those attachments have little to no overview and can be downloaded by almost anyone, which has been abused by attackers to host malicious payloads.
- Effort: advanced
Dynamic DNS Contacted
Detect communication with dynamic dns domain. This kind of domain is often used by attackers. This rule can trigger false positive in non-controlled environment because dynamic dns is not always malicious.
- Effort: master
Enable Root Account With Dsenableroot
Detects when root is enabled. Attackers can use this as a mean of persistence since root is disabled by default.
- Effort: elementary
Exfiltration And Tunneling Tools Execution
Execution of well known tools for data exfiltration and tunneling
- Effort: advanced
Exfiltration Domain
Detects traffic toward a domain flagged as a possible exfiltration vector.
- Effort: master
FoggyWeb HTTP Default GET/POST Requests
Detects GET or POST request pattern observed within the first FoggyWeb campaign detected by Microsoft.
- Effort: advanced
GitLab CVE-2021-22205
Detects GitLab vulnerability CVE-2021-22205 exploitation success. It allows an attacker to do some remote code execution with user git. The HTTP return code 422 indicates a successfull exploitation.
- Effort: intermediate
HackTools Suspicious Names
Quick-win rule to detect the default process names or file names of several HackTools.
- Effort: advanced
Kernel Module Alteration
Kernel module installation can be used to configure system settings to automatically execute a program during system boot or logon to maintain persistence or gain higher-level privileges on compromised systems. The prerequisites are to enable monitoring of the finit_module, init_module, delete_module syscalls using Auditbeat.
- Effort: advanced
Koadic MSHTML Command
Detects Koadic payload using MSHTML module
- Effort: intermediate
LokiBot Default C2 URL
Detects default C2 URL for trojan LokiBot
- Effort: elementary
Network Scanning and Discovery
Tools and command lines used for network discovery from current system
- Effort: advanced
Network Sniffing
List of common tools used for network packages sniffing
- Effort: advanced
Network Sniffing Windows
Network sniffing refers to using the network interface on a system to monitor or capture information sent over a wired or wireless connection. An adversary may place a network interface into promiscuous mode to passively access data in transit over the network, or use span ports to capture a larger amount of data.
- Effort: intermediate
NlTest Usage
Detects attempts to gather information on domain trust relationships that may be used to identify lateral movement opportunities. These command lines were observed in numerous attacks, but also sometimes from legitimate administrators for debugging purposes. The rule does not cover very basics commands but rather the ones that are interesting for attackers to gather information on a domain.
- Effort: advanced
PasswordDump SecurityXploded Tool
Detects the execution of the PasswordDump SecurityXploded Tool
- Effort: elementary
Possible Malicious File Double Extension
Detects request to potential malicious file with double extension
- Effort: elementary
Potential Azure AD Phishing Page (Adversary-in-the-Middle)
Detects an HTTP request to an URL typical of the Azure AD authentication flow, but towards a domain that is not one the legitimate Microsoft domains used for Azure AD authentication.
- Effort: intermediate
Privilege Escalation Awesome Scripts (PEAS)
Detect PEAS privileges escalation scripts and binaries
- Effort: elementary
ProxyShell Microsoft Exchange Suspicious Paths
Detects suspicious calls to Microsoft Exchange resources, in locations related to webshells observed in campaigns using this vulnerability.
- Effort: elementary
PsExec Process
Detects PsExec execution, command line which contains pstools or installation of the PsExec service. PsExec is a SysInternals which can be used to execute a program on another computer. The tool is as much used by attackers as by administrators.
- Effort: advanced
RDP Session Discovery
Detects use of RDP session discovery via qwinsta or quser. Used by some threat actors to know if someone is working via RDP on a server.
- Effort: advanced
RTLO Character
Detects RTLO (Right-To-Left character) in file and process names.
- Effort: elementary
Raccoon Stealer 2.0 Legitimate Third-Party DLL Download URL
Detects Raccoon Stealer 2.0 malware downloading legitimate third-party DLLs from its C2 server. These legitimate DLLs are used by the information stealer to collect data on the compromised hosts.
- Effort: elementary
Remote Access Tool Domain
Detects traffic toward a domain flagged as a Remote Administration Tool (RAT).
- Effort: master
Remote Monitoring and Management Software - AnyDesk
Detect artifacts related to the installation or execution of the Remote Monitoring and Management tool AnyDesk.
- Effort: master
Remote Monitoring and Management Software - Atera
Detect artifacts related to the installation or execution of the Remote Monitoring and Management tool Atera.
- Effort: master
SEKOIA.IO Intelligence Feed
Detect threats based on indicators of compromise (IOCs) collected by SEKOIA's Threat and Detection Research team.
- Effort: elementary
Sekoia.io EICAR Detection
Detects observables in Sekoia.io CTI tagged as EICAR, which are fake samples meant to test detection.
- Effort: master
SharePoint Authenticated SSRF
Detects succesful SSRF from an authenticated SharePoint user.
- Effort: elementary
Suspicious Double Extension
Detects suspicious use of an .exe extension after a non-executable file extension like .pdf.exe, a set of spaces or underlines to cloak the executable file in spearphishing campaigns
- Effort: advanced
Suspicious Download Links From Legitimate Services
Detects users clicking on Google docs links to download suspicious files. This technique was used a lot by Bazar Loader in the past.
- Effort: intermediate
Suspicious TOR Gateway
Detects suspicious TOR gateways. Gateways are often used by the victim to pay and decrypt the encrypted files without installing TOR. Tor intercepts the network traffic from one or more apps on user’s computer, usually the user web browser, and shuffles it through a number of randomly-chosen computers before passing it on to its destination. This disguises user location, and makes it harder for servers to pick him/her out on repeat visits, or to tie together separate visits to different sites, this making tracking and surveillance more difficult. Before a network packet starts its journey, user’s computer chooses a random list of relays and repeatedly encrypts the data in multiple layers, like an onion. Each relay knows only enough to strip off the outermost layer of encryption, before passing what’s left on to the next relay in the list.
- Effort: advanced
Suspicious URI Used In A Lazarus Campaign
Detects suspicious requests to a specific URI, usually on an .asp page. The website is often compromised.
- Effort: intermediate
System Info Discovery
System info discovery, attempt to detects basic command use to fingerprint a host.
- Effort: master
TOR Usage Generic Rule
Detects TOR usage globally, whether the IP is a destination or source. TOR is short for The Onion Router, and it gets its name from how it works. TOR intercepts the network traffic from one or more apps on user’s computer, usually the user web browser, and shuffles it through a number of randomly-chosen computers before passing it on to its destination. This disguises user location, and makes it harder for servers to pick him/her out on repeat visits, or to tie together separate visits to different sites, this making tracking and surveillance more difficult. Before a network packet starts its journey, user’s computer chooses a random list of relays and repeatedly encrypts the data in multiple layers, like an onion. Each relay knows only enough to strip off the outermost layer of encryption, before passing what’s left on to the next relay in the list.
- Effort: master
Event Categories
The following table lists the data source offered by this integration.
| Data Source | Description |
|---|---|
Asset management |
Unregistered Device Log Messages expose exported XML device inventory context. |
Authentication logs |
WorkPlace Logs provide portal shortcut and authorization troubleshooting telemetry. |
Host network interface |
Network Tunnel Audit Log captures tunnel and flow records, including bracketed variants, with endpoint metadata. |
Network device configuration |
Management Audit Log records administrative configuration changes. |
Network device logs |
System Message Log provides core system/service telemetry and policy decision traces. |
Network protocol analysis |
Resource Access Log captures allow or deny decisions for source to destination resource connections. |
Services |
Management Message Log provides AMC operational telemetry, including cron-command variants. |
Web logs |
Management Access Log captures administrative console HTTP access. |
Web proxy |
Web Proxy Audit Log captures proxy HTTP access records. |
In details, the following table denotes the type of events produced by this integration.
| Name | Values |
|---|---|
| Kind | event |
| Category | authentication, configuration, host, iam, network |
| Type | change, connection, info |
Transformed Events Samples after Ingestion
This section demonstrates how the raw logs will be transformed by our parsers. It shows the extracted fields that will be available for use in the built-in detection rules and hunting activities in the events page. Understanding these transformations is essential for analysts to create effective detection mechanisms with custom detection rules and to leverage the full potential of the collected data.
{
    "message": "127.0.0.1 - admin [25/Jul/2025:05:30:52 -0700] \"GET /Console/PendingChanges HTTP/1.1\" 200 308",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.management_access",
        "kind": "event",
        "outcome": "success",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-07-25T12:30:52Z",
    "http": {
        "request": {
            "method": "GET"
        },
        "response": {
            "bytes": 308,
            "status_code": 200
        },
        "version": "1.1"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "127.0.0.1"
        ],
        "user": [
            "admin"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "console_action": "PendingChanges",
                "http_status_class": "2xx"
            }
        }
    },
    "source": {
        "address": "127.0.0.1",
        "ip": "127.0.0.1"
    },
    "url": {
        "path": "/Console/PendingChanges"
    },
    "user": {
        "name": "admin"
    }
}
{
    "message": "198.51.100.10 - - [01/Jul/2026:15:53:26 +0000] \"POST /j_security_check HTTP/1.1\" 303 0",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.management_access",
        "kind": "event",
        "outcome": "success",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-07-01T15:53:26Z",
    "http": {
        "request": {
            "method": "POST"
        },
        "response": {
            "bytes": 0,
            "status_code": 303
        },
        "version": "1.1"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.10"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "http_status_class": "3xx"
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10"
    },
    "url": {
        "path": "/j_security_check"
    }
}
{
    "message": "Info 6/3/2025 00:31:02 admin Applied configuration changes",
    "event": {
        "category": [
            "configuration"
        ],
        "dataset": "sonicwall.sma.1000.management_audit",
        "kind": "event",
        "severity": 6,
        "type": [
            "change"
        ]
    },
    "@timestamp": "2025-06-03T00:31:02Z",
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "user": [
            "admin"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "change_type": "configuration"
            }
        }
    },
    "user": {
        "name": "admin"
    }
}
{
    "message": "2025-07-25T12:31:06+00:00 AMC@gateway01.example.com local4.info AMC: 2025-07-25 12:31:06 +0000 INFO com.aventail.mgmt.rest.console.centralmanagement.managed.sharedstate.TrafficOptimizerConfigurationResource12_2 - Clearing traffic optimizer configuration",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "provider": "AMC:",
        "severity": 6,
        "start": "2025-07-25T12:31:06Z",
        "timezone": "+0000",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-07-25T12:31:06Z",
    "log": {
        "level": "info"
    },
    "observer": {
        "hostname": "gateway01.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "gateway01.example.com"
        ]
    },
    "service": {
        "name": "AMC"
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "management": {
                    "class_name": "com.aventail.mgmt.rest.console.centralmanagement.managed.sharedstate.TrafficOptimizerConfigurationResource12_2"
                },
                "syslog_facility": "local4"
            }
        }
    }
}
{
    "message": "2026-07-01 15:53:26 +0000 INFO    [admin]: Login succeeded - Address=198.51.100.10",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-07-01T15:53:26Z",
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.10"
        ],
        "user": [
            "admin"
        ]
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10"
    },
    "user": {
        "name": "admin"
    }
}
{
    "message": "pam_unix(cron:session): session closed for user root",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "provider": "cron",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "user": [
            "root"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "unix_auth": {
                    "context_type": "session"
                }
            }
        }
    },
    "user": {
        "name": "root"
    }
}
{
    "message": "2026-07-02 14:33:15 +0000 INFO    [admin]: Adding user group - Name=grp4\n",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-07-02T14:33:15Z",
    "group": {
        "name": "grp4"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "user": [
            "admin"
        ]
    },
    "user": {
        "name": "admin"
    }
}
{
    "message": "2026-07-02 14:48:12 +0000 ERROR     com.aventail.mgmt.jetty.JettyServer - SSL handshake failed: Closed during handshake (198.51.100.10:40236)",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "severity": 3,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-07-02T14:48:12Z",
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.10"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "management": {
                    "class_name": "com.aventail.mgmt.jetty.JettyServer"
                }
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10",
        "port": 40236
    }
}
{
    "message": "2026-07-02 14:52:48 +0000 INFO    [admin]: Added address pool - ID=ID1111111111111111 Name=Test Example",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-07-02T14:52:48Z",
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "user": [
            "admin"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "management": {
                    "address_pool": {
                        "id": "ID1111111111111111",
                        "name": "Test Example"
                    }
                }
            }
        }
    },
    "user": {
        "name": "admin"
    }
}
{
    "message": "(root) CMD (   run-parts --report /etc/cron.hourly > /dev/null 2>&1)",
    "event": {
        "action": "scheduled-command",
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.management_message",
        "kind": "event",
        "provider": "cron",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "command_line": "   run-parts --report /etc/cron.hourly > /dev/null 2>&1"
    },
    "related": {
        "user": [
            "root"
        ]
    },
    "user": {
        "name": "root"
    }
}
{
    "message": "[::ffff:198.51.100.10]:59234 - \"(user02)@(CT)\" \"31/Jul/2025:14:41:23.073 +0530\" 1.2 tunnel 203.0.113.20 -1 112639 137450 165 W\"42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24\"",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.network_tunnel",
        "duration": 165000000000,
        "kind": "event",
        "outcome": "success",
        "type": [
            "connection"
        ]
    },
    "@timestamp": "2025-07-31T09:11:23.073000Z",
    "destination": {
        "address": "203.0.113.20",
        "bytes": 137450,
        "ip": "203.0.113.20"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "W"
    },
    "related": {
        "ip": [
            "198.51.100.10",
            "203.0.113.20"
        ],
        "user": [
            "user02"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "connection_type": "tunnel",
                "equipment_id": "42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24",
                "tunnel_version": "1.2"
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "bytes": 112639,
        "ip": "198.51.100.10",
        "port": 59234,
        "user": {
            "domain": "CT",
            "name": "user02"
        }
    }
}
{
    "message": "198.51.100.10:59260 - \"(user02)@(CT)\" \"31/Jul/2025:14:40:47.815 +0530\" 1.2 flow:tcp 203.0.113.20:443 0 5436 129963 125 W\"42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24\"",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.network_tunnel",
        "duration": 125000000000,
        "kind": "event",
        "outcome": "success",
        "type": [
            "connection"
        ]
    },
    "@timestamp": "2025-07-31T09:10:47.815000Z",
    "destination": {
        "address": "203.0.113.20",
        "bytes": 129963,
        "ip": "203.0.113.20",
        "port": 443
    },
    "network": {
        "protocol": "tcp"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "W"
    },
    "related": {
        "ip": [
            "198.51.100.10",
            "203.0.113.20"
        ],
        "user": [
            "user02"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "connection_type": "flow:tcp",
                "equipment_id": "42 1a 69 3a 6c 75 ac eb-be 8a 0b 90 9b 13 c6 24",
                "tunnel_version": "1.2"
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "bytes": 5436,
        "ip": "198.51.100.10",
        "port": 59260,
        "user": {
            "domain": "CT",
            "name": "user02"
        }
    }
}
{
    "message": "[03/Sep/2026:11:04:57.514525 +0200] sma8200v-01.example.com 000000 kt 00000000 Info    Audit   Src='198.51.100.25:53083' User='(user.beta@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:TCP' Dest='203.0.113.175:7680' Error='0xffffffff' SrcBytes='52' DstBytes='0' Duration='0' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7890.' SessionKey='SMA8200v:6a992741:00000000'",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.network_tunnel",
        "duration": 0,
        "kind": "event",
        "outcome": "failure",
        "severity": 6,
        "type": [
            "connection"
        ]
    },
    "@timestamp": "2026-09-03T09:04:57.514525Z",
    "destination": {
        "address": "203.0.113.175",
        "bytes": 0,
        "ip": "203.0.113.175",
        "port": 7680
    },
    "network": {
        "protocol": "tcp"
    },
    "observer": {
        "hostname": "sma8200v-01.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "W",
        "pid": 0
    },
    "related": {
        "hosts": [
            "sma8200v-01.example.com"
        ],
        "ip": [
            "198.51.100.25",
            "203.0.113.175"
        ],
        "user": [
            "user.beta@example.com"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "kt",
                "connection_type": "flow:tcp",
                "equipment_id": "0100_0000_0000_0000_ABCD_EF12_3456_7890.",
                "source_id": "00000000",
                "tunnel_version": "0x102"
            }
        }
    },
    "source": {
        "address": "198.51.100.25",
        "bytes": 52,
        "ip": "198.51.100.25",
        "port": 53083,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.beta@example.com",
            "name": "user.beta@example.com"
        }
    }
}
{
    "message": "EventMessage: Resource Access - User='(user.alpha@example.com)@(EXAMPLE_ORG)', Src='198.51.100.10:43496', Dest_IP='203.0.113.56:53', Rule Info='DEFAULT RULES', Full Destination='203.0.113.56:53', Access Agent='-', Allowed='1'",
    "event": {
        "action": "resource-access",
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.resource_access",
        "kind": "event",
        "outcome": "success",
        "type": [
            "connection"
        ]
    },
    "destination": {
        "address": "203.0.113.56",
        "ip": "203.0.113.56",
        "port": 53
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.10",
            "203.0.113.56"
        ],
        "user": [
            "user.alpha@example.com"
        ]
    },
    "rule": {
        "name": "DEFAULT RULES"
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10",
        "port": 43496,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.alpha@example.com",
            "name": "user.alpha@example.com"
        }
    },
    "user": {
        "domain": "EXAMPLE_ORG",
        "email": "user.alpha@example.com",
        "name": "user.alpha@example.com"
    }
}
{
    "message": "EventMessage: Resource Access - User='(user.beta@example.com)@(EXAMPLE_ORG)', Src='198.51.100.11:52532', Dest_IP='203.0.113.239:7680', Rule Info='-', Full Destination='host-a.internal.example.com:7680', Access Agent='-', Allowed='0'",
    "event": {
        "action": "resource-access",
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.resource_access",
        "kind": "event",
        "outcome": "failure",
        "type": [
            "connection"
        ]
    },
    "destination": {
        "address": "host-a.internal.example.com",
        "domain": "host-a.internal.example.com",
        "ip": "203.0.113.239",
        "port": 7680,
        "registered_domain": "example.com",
        "subdomain": "host-a.internal",
        "top_level_domain": "com"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "host-a.internal.example.com"
        ],
        "ip": [
            "198.51.100.11",
            "203.0.113.239"
        ],
        "user": [
            "user.beta@example.com"
        ]
    },
    "source": {
        "address": "198.51.100.11",
        "ip": "198.51.100.11",
        "port": 52532,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.beta@example.com",
            "name": "user.beta@example.com"
        }
    },
    "user": {
        "domain": "EXAMPLE_ORG",
        "email": "user.beta@example.com",
        "name": "user.beta@example.com"
    }
}
{
    "message": "EventMessage: Resource Access - User='(user.gamma@example.com)@(EXAMPLE_ORG)', Src='198.51.100.12:53210', Dest_IP='203.0.113.120:7680', Rule Info='TOULOUSE RULES', Full Destination='host-b.internal.example.com:7680', Access Agent='-', Allowed='1'",
    "event": {
        "action": "resource-access",
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.resource_access",
        "kind": "event",
        "outcome": "success",
        "type": [
            "connection"
        ]
    },
    "destination": {
        "address": "host-b.internal.example.com",
        "domain": "host-b.internal.example.com",
        "ip": "203.0.113.120",
        "port": 7680,
        "registered_domain": "example.com",
        "subdomain": "host-b.internal",
        "top_level_domain": "com"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "host-b.internal.example.com"
        ],
        "ip": [
            "198.51.100.12",
            "203.0.113.120"
        ],
        "user": [
            "user.gamma@example.com"
        ]
    },
    "rule": {
        "name": "TOULOUSE RULES"
    },
    "source": {
        "address": "198.51.100.12",
        "ip": "198.51.100.12",
        "port": 53210,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.gamma@example.com",
            "name": "user.gamma@example.com"
        }
    },
    "user": {
        "domain": "EXAMPLE_ORG",
        "email": "user.gamma@example.com",
        "name": "user.gamma@example.com"
    }
}
{
    "message": "EventMessage: Resource Access - User='(user.delta@example.com)@(EXAMPLE_ORG)', Src='198.51.100.13:53211', Dest_IP='203.0.113.121:389', Rule Info='-', Full Destination='203.0.113.121:389', Access Agent='-', Allowed='0'",
    "event": {
        "action": "resource-access",
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.resource_access",
        "kind": "event",
        "outcome": "failure",
        "type": [
            "connection"
        ]
    },
    "destination": {
        "address": "203.0.113.121",
        "ip": "203.0.113.121",
        "port": 389
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.13",
            "203.0.113.121"
        ],
        "user": [
            "user.delta@example.com"
        ]
    },
    "source": {
        "address": "198.51.100.13",
        "ip": "198.51.100.13",
        "port": 53211,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.delta@example.com",
            "name": "user.delta@example.com"
        }
    },
    "user": {
        "domain": "EXAMPLE_ORG",
        "email": "user.delta@example.com",
        "name": "user.delta@example.com"
    }
}
{
    "message": "[03/Sep/2026:11:04:58.123456 +0200] sma8200v-02.example.com 000000 kt 00000000 Info    Audit   Src='198.51.100.30:54001' User='(user.gamma@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:TCP' Dest='203.0.113.88:443' Error='0' SrcBytes='1024' DstBytes='2048' Duration='9' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7891.' SessionKey='SMA8200v:6a992742:00000000'",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.network_tunnel",
        "duration": 9000000000,
        "kind": "event",
        "outcome": "success",
        "severity": 6,
        "type": [
            "connection"
        ]
    },
    "@timestamp": "2026-09-03T09:04:58.123456Z",
    "destination": {
        "address": "203.0.113.88",
        "bytes": 2048,
        "ip": "203.0.113.88",
        "port": 443
    },
    "network": {
        "protocol": "tcp"
    },
    "observer": {
        "hostname": "sma8200v-02.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "W",
        "pid": 0
    },
    "related": {
        "hosts": [
            "sma8200v-02.example.com"
        ],
        "ip": [
            "198.51.100.30",
            "203.0.113.88"
        ],
        "user": [
            "user.gamma@example.com"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "kt",
                "connection_type": "flow:tcp",
                "equipment_id": "0100_0000_0000_0000_ABCD_EF12_3456_7891.",
                "source_id": "00000000",
                "tunnel_version": "0x102"
            }
        }
    },
    "source": {
        "address": "198.51.100.30",
        "bytes": 1024,
        "ip": "198.51.100.30",
        "port": 54001,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.gamma@example.com",
            "name": "user.gamma@example.com"
        }
    }
}
{
    "message": "[03/Sep/2026:11:04:59.654321 +0200] sma8200v-03.example.com 000000 kt 00000000 Info    Audit   Src='198.51.100.31:54002' User='(user.delta@example.com)@(EXAMPLE_ORG)' TunnelVersion='0x102' Command='Flow:UDP' Dest='203.0.113.89:5353' Error='0xffffff92' SrcBytes='512' DstBytes='256' Duration='3' PlatformPrefix='W' EquipmentId='0100_0000_0000_0000_ABCD_EF12_3456_7892.' SessionKey='SMA8200v:6a992743:00000000'",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.network_tunnel",
        "duration": 3000000000,
        "kind": "event",
        "outcome": "failure",
        "severity": 6,
        "type": [
            "connection"
        ]
    },
    "@timestamp": "2026-09-03T09:04:59.654321Z",
    "destination": {
        "address": "203.0.113.89",
        "bytes": 256,
        "ip": "203.0.113.89",
        "port": 5353
    },
    "network": {
        "protocol": "udp"
    },
    "observer": {
        "hostname": "sma8200v-03.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "W",
        "pid": 0
    },
    "related": {
        "hosts": [
            "sma8200v-03.example.com"
        ],
        "ip": [
            "198.51.100.31",
            "203.0.113.89"
        ],
        "user": [
            "user.delta@example.com"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "kt",
                "connection_type": "flow:udp",
                "equipment_id": "0100_0000_0000_0000_ABCD_EF12_3456_7892.",
                "source_id": "00000000",
                "tunnel_version": "0x102"
            }
        }
    },
    "source": {
        "address": "198.51.100.31",
        "bytes": 512,
        "ip": "198.51.100.31",
        "port": 54002,
        "user": {
            "domain": "EXAMPLE_ORG",
            "email": "user.delta@example.com",
            "name": "user.delta@example.com"
        }
    }
}
{
    "message": "[29/Jul/2025:14:02:38.051761 +0000] gateway-kernel-01.example.com 000000 kp 0000020a Internal Misc <KERNEL> created channel (pid=6268):0000000021ce9936",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.system",
        "kind": "event",
        "severity": 0,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-07-29T14:02:38.051761Z",
    "observer": {
        "hostname": "gateway-kernel-01.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "kp",
        "pid": 6268
    },
    "related": {
        "hosts": [
            "gateway-kernel-01.example.com"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "kp",
                "source_id": "0000020a"
            }
        }
    }
}
{
    "message": "[6/3/2025 00:32:36.115] E-Class SMASSLVPN 002421 ps 100004b3 Info EWACL User ' (198.51.100.10 (user-example)@(group01)' connecting from '198.51.100.10:37975' matched rule 'accessRule(AV1091719670706:preauth access rule)', access to '127.0.0.1:455' is permitted.",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.system",
        "kind": "event",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-03T00:32:36.115000Z",
    "destination": {
        "address": "127.0.0.1",
        "ip": "127.0.0.1",
        "port": 455
    },
    "observer": {
        "hostname": "E-Class SMASSLVPN",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "ps",
        "pid": 2421
    },
    "related": {
        "hosts": [
            "E-Class SMASSLVPN"
        ],
        "ip": [
            "127.0.0.1",
            "198.51.100.10"
        ]
    },
    "rule": {
        "id": "AV1091719670706",
        "name": "preauth access rule"
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "ps",
                "policy": {
                    "log_type": "EWACL"
                },
                "source_id": "100004b3"
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10",
        "port": 37975
    }
}
{
    "message": "[6/3/2025 00:32:36.115 +0000] E-Class SMASSLVPN 027186 uk 00000001 Verbose System ::API::FAKEA145dFYNZimCKNWHB7p2q2Y=::(user01)@(group01)::CLIENT:: Interrogation: Evaluation of OPSWATAV AV1128462569762A [NortonAV.dll,Symantec Corp.,Symantec Client Security,>=,9.x,,,,,FALSE] results: FALSE",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.system",
        "kind": "event",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-03T00:32:36.115000Z",
    "observer": {
        "hostname": "E-Class SMASSLVPN",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "uk",
        "pid": 27186
    },
    "related": {
        "hosts": [
            "E-Class SMASSLVPN"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "uk",
                "epc": {
                    "query_result": "FALSE"
                },
                "source_id": "00000001"
            }
        }
    }
}
{
    "message": "[02/Jul/2025:18:47:29.113075 +0000] SMAnode 013581 ps 00000000 Info System Auth: CRL-CERT: Cert verification status = 0, err = 19, reason = 'self-signed certificate in certificate chain', subject='/C=US/ST=Washington/L=Seattle/O=SonicWall/OU=Engineering/CN=Untrusted CA'",
    "event": {
        "category": [
            "host"
        ],
        "dataset": "sonicwall.sma.1000.system",
        "kind": "event",
        "severity": 6,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-07-02T18:47:29.113075Z",
    "observer": {
        "hostname": "SMAnode",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "process": {
        "name": "ps",
        "pid": 13581
    },
    "related": {
        "hosts": [
            "SMAnode"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "app_id": "ps",
                "certificate": {
                    "error_code": 19,
                    "error_reason": "self-signed certificate in certificate chain"
                },
                "source_id": "00000000"
            }
        }
    }
}
{
    "message": "https://gateway.internal.example.com:8443/UnregisteredDevices.xml",
    "event": {
        "category": [
            "iam"
        ],
        "dataset": "sonicwall.sma.1000.unregistered_device",
        "kind": "event",
        "type": [
            "info"
        ]
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    }
}
{
    "message": "https://gateway.internal.example.com:8443/UnregisteredDevices.xml?lastLoginTime=2026-08-07T12:00:00Z&platform=Windows&realm=Students&username=user.test&exported=true&deviceCount=10&limit=100",
    "event": {
        "category": [
            "iam"
        ],
        "dataset": "sonicwall.sma.1000.unregistered_device",
        "kind": "event",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2026-08-07T12:00:00Z",
    "host": {
        "os": {
            "type": "windows"
        }
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "user": [
            "user.test"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "export_state": "true",
                "registered_device_count": 10,
                "unregistered_device": {
                    "limit": 100
                }
            }
        }
    },
    "user": {
        "domain": "Students",
        "name": "user.test"
    }
}
{
    "message": "198.51.100.10 - (user01)@(AD) [6/3/2025 00:32:36.115 +0000] \"GET /workplace/access/home HTTP/1.1\" 200 15424",
    "event": {
        "category": [
            "network"
        ],
        "dataset": "sonicwall.sma.1000.web_proxy",
        "kind": "event",
        "outcome": "success",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-03T00:32:36.115000Z",
    "http": {
        "request": {
            "method": "GET"
        },
        "response": {
            "bytes": 15424,
            "status_code": 200
        },
        "version": "1.1"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "198.51.100.10"
        ],
        "user": [
            "user01"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "api_endpoint": "/workplace/access/home",
                "http_status_class": "2xx"
            }
        }
    },
    "source": {
        "address": "198.51.100.10",
        "ip": "198.51.100.10",
        "user": {
            "domain": "AD",
            "name": "user01"
        }
    },
    "url": {
        "path": "/workplace/access/home"
    }
}
{
    "message": "2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:24 +0530 DEBUG - GOT: CredentialsManager[teamSessionId=FAKESESSIONID7QuQWL3BGdokQ==,teamcredentials={username=user01} ,credentials={}]",
    "event": {
        "category": [
            "authentication",
            "network"
        ],
        "dataset": "sonicwall.sma.1000.workplace",
        "kind": "event",
        "provider": "WP:",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-30T08:47:23Z",
    "log": {
        "level": "debug"
    },
    "observer": {
        "hostname": "client-gateway.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "client-gateway.example.com"
        ],
        "user": [
            "user01"
        ]
    },
    "service": {
        "name": "WP"
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "workplace": {
                    "team_session_id": "FAKESESSIONID7QuQWL3BGdokQ=="
                }
            }
        }
    },
    "user": {
        "name": "user01"
    }
}
{
    "message": "2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:23 +0530 DEBUG - PolicyClientSession: <authorize:exit> uri=http://127.0.0.1:8085/ctdownload/ status=PCL_STATUS_SUCCESS",
    "event": {
        "action": "authorize:exit",
        "category": [
            "authentication",
            "network"
        ],
        "dataset": "sonicwall.sma.1000.workplace",
        "kind": "event",
        "outcome": "success",
        "provider": "WP:",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-30T08:47:23Z",
    "log": {
        "level": "debug"
    },
    "observer": {
        "hostname": "client-gateway.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "client-gateway.example.com"
        ]
    },
    "service": {
        "name": "WP"
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "workplace": {
                    "policy_status": "PCL_STATUS_SUCCESS",
                    "shortcut_type": "web"
                }
            }
        }
    },
    "url": {
        "domain": "127.0.0.1",
        "full": "http://127.0.0.1:8085/ctdownload/",
        "original": "http://127.0.0.1:8085/ctdownload/",
        "path": "/ctdownload/",
        "port": 8085,
        "scheme": "http"
    }
}
{
    "message": "2025-06-30T14:17:23+05:30 127.0.0.1/127.0.0.1 local7.debug DEBUG [22:03:03,617] pcsession: <authorize:exit> uri=smb://fileshare01.example.com/marketing status=SUCCESS",
    "event": {
        "action": "authorize:exit",
        "category": [
            "authentication",
            "network"
        ],
        "dataset": "sonicwall.sma.1000.workplace",
        "kind": "event",
        "outcome": "success",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-30T08:47:23Z",
    "log": {
        "level": "debug"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "127.0.0.1"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "workplace": {
                    "policy_status": "SUCCESS",
                    "shortcut_type": "network"
                }
            }
        }
    },
    "source": {
        "address": "127.0.0.1",
        "ip": "127.0.0.1"
    },
    "url": {
        "domain": "fileshare01.example.com",
        "original": "smb://fileshare01.example.com/marketing",
        "path": "/marketing",
        "registered_domain": "example.com",
        "scheme": "smb",
        "subdomain": "fileshare01",
        "top_level_domain": "com"
    }
}
{
    "message": "2025-06-30T14:17:23+05:30 127.0.0.1/127.0.0.1 local7.debug DEBUG [22:12:15,043] pcsession: <authorize:exit> uri=http://app.internal.example.com status=FAILURE",
    "event": {
        "action": "authorize:exit",
        "category": [
            "authentication",
            "network"
        ],
        "dataset": "sonicwall.sma.1000.workplace",
        "kind": "event",
        "outcome": "failure",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-30T08:47:23Z",
    "log": {
        "level": "debug"
    },
    "observer": {
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "ip": [
            "127.0.0.1"
        ]
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "workplace": {
                    "policy_status": "FAILURE",
                    "shortcut_type": "web"
                }
            }
        }
    },
    "source": {
        "address": "127.0.0.1",
        "ip": "127.0.0.1"
    },
    "url": {
        "domain": "app.internal.example.com",
        "full": "http://app.internal.example.com",
        "original": "http://app.internal.example.com",
        "port": 80,
        "registered_domain": "example.com",
        "scheme": "http",
        "subdomain": "app.internal",
        "top_level_domain": "com"
    }
}
{
    "message": "2025-06-30T14:17:23+05:30 WP@client-gateway.example.com local7.debug WP: 2025-06-30 14:17:23 +0530 DEBUG - PolicyClientSession: <authorize:exit> uri=http://127.0.0.1:8085/ctdownload/ status=PCL_STATUS_SUCCESa",
    "event": {
        "action": "authorize:exit",
        "category": [
            "authentication",
            "network"
        ],
        "dataset": "sonicwall.sma.1000.workplace",
        "kind": "event",
        "provider": "WP:",
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-06-30T08:47:23Z",
    "log": {
        "level": "debug"
    },
    "observer": {
        "hostname": "client-gateway.example.com",
        "product": "Secure Mobile Access",
        "type": "firewall",
        "vendor": "SonicWall"
    },
    "related": {
        "hosts": [
            "client-gateway.example.com"
        ]
    },
    "service": {
        "name": "WP"
    },
    "sonicwall": {
        "sma": {
            "1000": {
                "workplace": {
                    "policy_status": "PCL_STATUS_SUCCESa",
                    "shortcut_type": "web"
                }
            }
        }
    },
    "url": {
        "domain": "127.0.0.1",
        "full": "http://127.0.0.1:8085/ctdownload/",
        "original": "http://127.0.0.1:8085/ctdownload/",
        "path": "/ctdownload/",
        "port": 8085,
        "scheme": "http"
    }
}
Extracted Fields
The following table lists the fields that are extracted, normalized under the ECS format, analyzed and indexed by the parser. It should be noted that infered fields are not listed.
| Name | Type | Description |
|---|---|---|
@timestamp |
date |
Date/time when the event originated. |
destination.bytes |
long |
Bytes sent from the destination to the source. |
destination.domain |
keyword |
The domain name of the destination. |
destination.ip |
ip |
IP address of the destination. |
destination.port |
long |
Port of the destination. |
event.action |
keyword |
The action captured by the event. |
event.category |
keyword |
Event category. The second categorization field in the hierarchy. |
event.dataset |
keyword |
Name of the dataset. |
event.duration |
long |
Duration of the event in nanoseconds. |
event.kind |
keyword |
The kind of the event. The highest categorization field in the hierarchy. |
event.outcome |
keyword |
The outcome of the event. The lowest level categorization field in the hierarchy. |
event.provider |
keyword |
Source of the event. |
event.severity |
long |
Numeric severity of the event. |
event.start |
date |
event.start contains the date when the event started or when the activity was first observed. |
event.timezone |
keyword |
Event time zone. |
event.type |
keyword |
Event type. The third categorization field in the hierarchy. |
group.name |
keyword |
Name of the group. |
host.os.type |
keyword |
Which commercial OS family (one of: linux, macos, unix or windows). |
http.request.method |
keyword |
HTTP request method. |
http.response.bytes |
long |
Total size in bytes of the response (body and headers). |
http.response.status_code |
long |
HTTP response status code. |
http.version |
keyword |
HTTP version. |
log.level |
keyword |
Log level of the log event. |
message |
match_only_text |
Log message optimized for viewing in a log viewer. |
network.protocol |
keyword |
Application protocol name. |
observer.hostname |
keyword |
Hostname of the observer. |
observer.product |
keyword |
The product name of the observer. |
observer.type |
keyword |
The type of the observer the data is coming from. |
observer.vendor |
keyword |
Vendor name of the observer. |
process.command_line |
wildcard |
Full command line that started the process. |
process.name |
keyword |
Process name. |
process.pid |
long |
Process id. |
rule.id |
keyword |
Rule ID |
rule.name |
keyword |
Rule name |
service.name |
keyword |
Name of the service. |
sonicwall.sma.1000.api_endpoint |
keyword |
Extracted HTTP endpoint path for proxy requests |
sonicwall.sma.1000.app_id |
keyword |
Application or service identifier found in system message logs |
sonicwall.sma.1000.certificate.error_code |
long |
Certificate verification error code from client certificate checks |
sonicwall.sma.1000.certificate.error_reason |
keyword |
Certificate verification error reason from client certificate checks |
sonicwall.sma.1000.change_type |
keyword |
Derived category of management audit change |
sonicwall.sma.1000.connection_type |
keyword |
Connection family for network tunnel logs such as tunnel or flow protocol |
sonicwall.sma.1000.console_action |
keyword |
Derived management console action from requested URL path |
sonicwall.sma.1000.epc.query_result |
keyword |
Endpoint control interrogation evaluation result |
sonicwall.sma.1000.equipment_id |
keyword |
Equipment identifier emitted in network tunnel audit logs |
sonicwall.sma.1000.export_state |
keyword |
Exported or unexported selector from unregistered device URL parameters |
sonicwall.sma.1000.http_status_class |
keyword |
Derived HTTP response class such as 2xx, 3xx, 4xx, or 5xx |
sonicwall.sma.1000.management.address_pool.id |
keyword |
Address pool identifier extracted from management plain messages |
sonicwall.sma.1000.management.address_pool.name |
keyword |
Address pool name extracted from management plain messages |
sonicwall.sma.1000.management.class_name |
keyword |
Java class name extracted from management service messages |
sonicwall.sma.1000.policy.log_type |
keyword |
Access policy log family indicator such as CSACL, EWACL, WPACL, or NEACL |
sonicwall.sma.1000.registered_device_count |
long |
Registered device count filter from unregistered device URL parameters |
sonicwall.sma.1000.source_id |
keyword |
Internal system source identifier token extracted from system message logs |
sonicwall.sma.1000.syslog_facility |
keyword |
Syslog facility extracted from management and workplace local facility labels |
sonicwall.sma.1000.tunnel_version |
keyword |
Tunnel protocol version from network tunnel audit logs |
sonicwall.sma.1000.unix_auth.context_type |
keyword |
PAM unix authentication context subtype extracted after the provider |
sonicwall.sma.1000.unregistered_device.limit |
long |
Maximum unregistered device entries requested in export URL |
sonicwall.sma.1000.workplace.policy_status |
keyword |
Raw policy status value observed in workplace authorization logs |
sonicwall.sma.1000.workplace.shortcut_type |
keyword |
Derived workplace shortcut type based on URI scheme |
sonicwall.sma.1000.workplace.team_session_id |
keyword |
Team session identifier extracted from workplace credential manager messages |
source.bytes |
long |
Bytes sent from the source to the destination. |
source.ip |
ip |
IP address of the source. |
source.port |
long |
Port of the source. |
source.user.domain |
keyword |
Name of the directory the user is a member of. |
source.user.email |
keyword |
User email address. |
source.user.name |
keyword |
Short name or login of the user. |
url.original |
wildcard |
Unmodified original url as seen in the event source. |
url.path |
wildcard |
Path of the request, such as "/search". |
user.domain |
keyword |
Name of the directory the user is a member of. |
user.email |
keyword |
User email address. |
user.name |
keyword |
Short name or login of the user. |
For more information on the Intake Format, please find the code of the Parser, Smart Descriptions, and Supported Events here.