Seckiot Citadelle
Overview
Seckiot Citadelle is an integrated cybersecurity platform designed for industrial control systems (ICS) and operational technology (OT) environments, providing comprehensive threat detection, asset discovery, and vulnerability management to safeguard critical infrastructure.
- Vendor: Seckiot
- Supported environment: On Premise & Cloud
- Version compatibility, if applicable: 25.5 and more
- Detection based on: Alerts, Telemetry
- Supported application or feature: Network protocol analysis
Specification
Prerequisites
- Network:
- Outbound traffic allowed
- Permissions:
- Administrator or Root access to the Seckiot Citadelle appliance
Transport Protocol/Method
- Direct HTTPS
Logs details
- Supported functionalities: See section Overview
- Supported type(s) of structure: JSON
- Supported verbosity level: Alert
Step-by-Step Configuration Procedure
Instruction on Sekoia
Configure Your Intake
This section will guide you through creating the intake object in Sekoia, which provides a unique identifier called the "Intake key." The Intake key is essential for later configuration, as it references the Community, Entity, and Parser (Intake Format) used when receiving raw events on Sekoia.
- Go to the Sekoia Intake page.
- Click on the
+ New Intakebutton at the top right of the page. - Search for your Intake by the product name in the search bar.
- Give it a Name and associate it with an Entity (and a Community if using multi-tenant mode).
- Click on
Create.
Note
For more details on how to use the Intake page and to find the Intake key you just created, refer to this documentation.
Configure Seckiot Alert Forwarding
- Log in to the Seckiot platform.
- In the left panel, click on
Capture architecture. -
Click on
Add -> Add a forwarder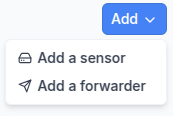
-
Select the forwarder type
Sekoia.io -
Enter a
Nameto identify the forwarder, then go back to the intake you created earlier in stepConfigure Your Intakein the Sekoia platform. Finally, copy your intake key into theIntake Keyfield.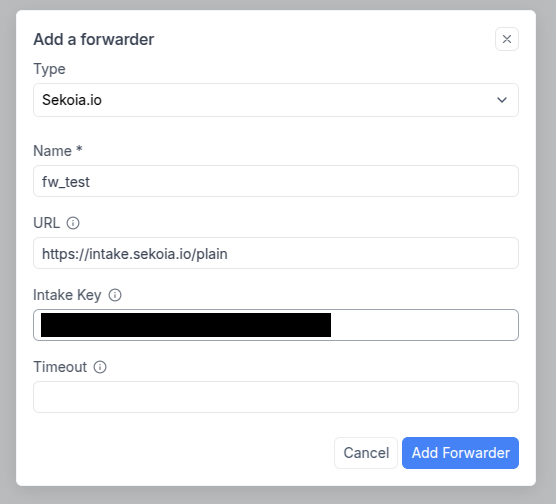
-
Click
Add Forwarder
Detection section
The following section provides information for those who wish to learn more about the detection capabilities enabled by collecting this intake. It includes details about the built-in rule catalog, event categories, and ECS fields extracted from raw events. This is essential for users aiming to create custom detection rules, perform hunting activities, or pivot in the events page.
Event Categories
The following table lists the data source offered by this integration.
| Data Source | Description |
|---|---|
Network intrusion detection system |
Seckiot Citadelle identify suspicious behaviors by providing alerts logs |
Network device logs |
The logs provided by Seckiot Citadelle give a good overview of the network activity |
Network protocol analysis |
The logs offered by Seckiot Citadelle provide traffic analysis |
Asset Management |
Seckiot Citadelle identify all devices and provide a complete visibility |
Transformed Events Samples after Ingestion
This section demonstrates how the raw logs will be transformed by our parsers. It shows the extracted fields that will be available for use in the built-in detection rules and hunting activities in the events page. Understanding these transformations is essential for analysts to create effective detection mechanisms with custom detection rules and to leverage the full potential of the collected data.
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T08:51:28.586238Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T08:51:28.586238Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"Fortinet, Inc.\",\"port\":58629,\"ip\":\"192.0.2.100\",\"mac\":\"02:00:00:00:00:05\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"first_seen\":\"2025-03-05T12:37:56.174487Z\",\"last_seen\":\"2025-03-12T08:50:59.469469Z\",\"name\":\"fw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"LANNER ELECTRONICS, INC.\",\"level\":\"2\",\"primary_ip\":\"11111111-1111-4111-8111-000000000011\",\"id\":\"11111111-1111-4111-8111-000000000014\",\"entity\":\"router\",\"description\":\"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T08:51:00.348Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000002\",\"alert_id\":\"11111111-1111-4111-8111-000000000003\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T08:51:28.586238Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"dns\"},\"@version\":\"1\",\"source\":{\"vendor\":\"LANNER ELECTRONICS, INC.\",\"port\":53,\"ip\":\"203.0.113.254\",\"mac\":\"02:00:00:00:00:04\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\",\"uuid\":\"51186749-7415-46be-90e5-000000000080\",\"name\":\"Network Service Discovery - UDP Scan Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "2",
                "3"
            ],
            "purdue_level": [
                2,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\": [], \"event\": {\"code\": [], \"severity\": 1, \"outcome\": \"unknown\", \"created\": \"2025-03-12T08:51:28.586238Z\", \"category\": [\"info\"], \"ingested\": \"2025-03-12T08:51:28.586238Z\", \"kind\": \"alert\", \"type\": [\"info\"]}, \"forwarders\": [\"fw_sekoiaIO\"], \"destination\": {\"vendor\": \"Fortinet, Inc.\", \"port\": 58629, \"ip\": \"192.0.2.100\", \"mac\": \"02:00:00:00:00:05\"}, \"skt\": {\"module\": \"Other\", \"sniffer\": \"11111111-1111-4111-8111-000000000010\", \"assets\": [{\"first_seen\": \"2025-03-05T12:37:56.174487Z\", \"last_seen\": \"2025-03-12T08:50:59.469469Z\", \"name\": \"fw01.example.com\", \"category\": \"IT\", \"hardware_vendor\": \"LANNER ELECTRONICS, INC.\", \"level\": 0, \"primary_ip\": \"11111111-1111-4111-8111-000000000011\", \"id\": \"11111111-1111-4111-8111-000000000014\", \"entity\": \"router\", \"description\": \"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\", \"localisation\": \"lab-192-0-2-101-ge-1-26.example.org\"}, {\"system\": \"Windows\", \"first_seen\": \"2025-03-05T12:37:56.077529Z\", \"last_seen\": \"2025-03-12T08:51:00.348Z\", \"name\": \"gw01.example.com\", \"category\": \"IT\", \"hardware_vendor\": \"VMware, Inc.\", \"level\": 3, \"primary_ip\": \"11111111-1111-4111-8111-000000000004\", \"id\": \"11111111-1111-4111-8111-000000000012\", \"entity\": \"router\", \"localisation\": \"lab-192-0-2-121-1-2-1.example.org\"}], \"capture_zone\": \"11111111-1111-4111-8111-000000000018\", \"session\": \"00000000000000000000000000000002\", \"alert_id\": \"11111111-1111-4111-8111-000000000003\", \"sensor\": \"SENSOR-0\"}, \"@timestamp\": \"2025-03-12T08:51:28.586238Z\", \"network\": {\"transport\": \"UDP\", \"protocol\": \"dns\"}, \"@version\": \"1\", \"source\": {\"vendor\": \"LANNER ELECTRONICS, INC.\", \"port\": 53, \"ip\": \"203.0.113.254\", \"mac\": \"02:00:00:00:00:04\"}, \"observer\": {\"name\": \"citadelle-01\", \"vendor\": \"Seckiot\", \"product\": \"Seckiot Citadelle\", \"_type\": \"NIDS\", \"version\": \"\"}, \"rule\": {\"description\": \"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\", \"uuid\": \"51186749-7415-46be-90e5-000000000080\", \"name\": \"Network Service Discovery - UDP Scan Port\", \"version\": \"1\", \"author\": \"Seckiot\"}}",
    "event": {
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Other",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "citadelle-01",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "0",
                "3"
            ],
            "purdue_level": [
                0,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Other",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T08:51:28.586238Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T08:51:28.586238Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"Fortinet, Inc.\",\"port\":58629,\"ip\":\"192.0.2.100\",\"mac\":\"02:00:00:00:00:05\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"first_seen\":\"2025-03-05T12:37:56.174487Z\",\"last_seen\":\"2025-03-12T08:50:59.469469Z\",\"name\":\"fw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"LANNER ELECTRONICS, INC.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000011\",\"id\":\"11111111-1111-4111-8111-000000000014\",\"entity\":\"router\",\"description\":\"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T08:51:00.348Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000002\",\"alert_id\":\"11111111-1111-4111-8111-000000000003\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T08:51:28.586238Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"dns\"},\"@version\":\"1\",\"source\":{\"vendor\":\"LANNER ELECTRONICS, INC.\",\"port\":53,\"ip\":\"203.0.113.254\",\"mac\":\"02:00:00:00:00:04\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\",\"uuid\":\"51186749-7415-46be-90e5-000000000080\",\"name\":\"Network Service Discovery - UDP Scan Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "3",
                "3"
            ],
            "purdue_level": [
                3,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T07:31:28.525356Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T07:31:28.525356Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"VMware, Inc.\",\"port\":4739,\"ip\":\"198.51.100.1\",\"mac\":\"02:00:00:00:00:02\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T07:31:12.375646Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"first_seen\":\"2025-03-06T13:57:58.838858Z\",\"last_seen\":\"2025-03-12T07:30:53.844522Z\",\"name\":\"fw02.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"Fortinet, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000020\",\"id\":\"11111111-1111-4111-8111-000000000001\",\"entity\":\"router\",\"description\":\"Firewall Site 2\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-05T12:37:53.554365Z\",\"last_seen\":\"2025-03-12T07:31:11.928426Z\",\"name\":\"srv02.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.4737\",\"primary_ip\":\"11111111-1111-4111-8111-000000000006\",\"id\":\"11111111-1111-4111-8111-000000000019\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"system\":\"Windows 2016+ Server\",\"first_seen\":\"2025-03-06T13:57:57.628789Z\",\"last_seen\":\"2025-03-12T07:31:21.084186Z\",\"name\":\"srv01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"version\":\"10.0.10011.16384\",\"primary_ip\":\"11111111-1111-4111-8111-000000000008\",\"id\":\"11111111-1111-4111-8111-000000000005\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-06T13:49:56.593575Z\",\"last_seen\":\"2025-03-12T07:31:12.347024Z\",\"name\":\"dc01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.379\",\"primary_ip\":\"11111111-1111-4111-8111-000000000013\",\"id\":\"11111111-1111-4111-8111-000000000002\",\"entity\":\"domain-controller\",\"description\":\"DC 1\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000003\",\"alert_id\":\"11111111-1111-4111-8111-000000000015\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T07:31:28.525356Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"iana_ipfix\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":8346,\"ip\":\"198.51.100.254\",\"mac\":\"02:00:00:00:00:01\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"A UDP flood Denial of Service attack involves sending a large number of UDP packets to random ports on a target. This overloads the target's network and resources, leading to performance degradation or unavailability of the service to legitimate users.\",\"uuid\":\"51186749-7415-46be-90e5-000000000087\",\"name\":\"Denial Of Service - UDP Flood\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T07:31:28.525356Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T07:31:28.525356Z",
    "destination": {
        "address": "198.51.100.1",
        "ip": "198.51.100.1",
        "mac": "02:00:00:00:00:02",
        "port": 4739
    },
    "device": {
        "manufacturer": [
            "Fortinet, Inc.",
            "VMware, Inc.",
            "VMware, Inc.",
            "VMware, Inc.",
            "VMware, Inc."
        ],
        "model": {
            "identifier": [
                "VMware7,1",
                "VMware7,1"
            ]
        }
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-111-gi0-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000001",
            "11111111-1111-4111-8111-000000000002",
            "11111111-1111-4111-8111-000000000005",
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000019"
        ],
        "name": [
            "dc01.example.com",
            "fw02.example.com",
            "gw01.example.com",
            "srv01.example.com",
            "srv02.example.com"
        ],
        "os": {
            "name": [
                "Windows",
                "Windows 2016+ Server",
                "Windows Server 2019 Standard",
                "Windows Server 2019 Standard"
            ],
            "version": [
                "10.0.10011.16384",
                "17763.379",
                "17763.4737"
            ]
        },
        "type": [
            "domain-controller",
            "router",
            "router",
            "virtual-server",
            "virtual-server"
        ]
    },
    "network": {
        "protocol": "iana_ipfix",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "198.51.100.1",
            "198.51.100.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "A UDP flood Denial of Service attack involves sending a large number of UDP packets to random ports on a target. This overloads the target's network and resources, leading to performance degradation or unavailability of the service to legitimate users.",
        "id": "51186749-7415-46be-90e5-000000000087",
        "name": "Denial Of Service - UDP Flood",
        "uuid": "51186749-7415-46be-90e5-000000000087",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000015"
        },
        "assets": {
            "category": [
                "IT",
                "IT",
                "IT",
                "IT",
                "IT"
            ],
            "description": [
                "DC 1",
                "Firewall Site 2"
            ],
            "entity": [
                "domain-controller",
                "router",
                "router",
                "virtual-server",
                "virtual-server"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000001",
                "11111111-1111-4111-8111-000000000002",
                "11111111-1111-4111-8111-000000000005",
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000019"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-111-gi0-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "dc01.example.com",
                "fw02.example.com",
                "gw01.example.com",
                "srv01.example.com",
                "srv02.example.com"
            ],
            "perdue_level": [
                "3",
                "3",
                "3",
                "3",
                "3"
            ],
            "purdue_level": [
                3,
                3,
                3,
                3,
                3
            ],
            "system": [
                "Windows",
                "Windows 2016+ Server",
                "Windows Server 2019 Standard",
                "Windows Server 2019 Standard"
            ],
            "version": [
                "10.0.10011.16384",
                "17763.379",
                "17763.4737"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000003"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "198.51.100.254",
        "ip": "198.51.100.254",
        "mac": "02:00:00:00:00:01",
        "port": 8346
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-12T13:34:04.407568Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T13:34:04.407568Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"\",\"assets\":[{\"name\":\"device01.example.com\",\"first_seen\":\"2025-03-12T13:33:48Z\",\"last_seen\":\"2025-03-12T13:34:04.348385Z\",\"id\":\"11111111-1111-4111-8111-000000000024\"}],\"capture_zone\":\"\",\"alert_id\":\"11111111-1111-4111-8111-000000000016\",\"sensor\":\"\"},\"@timestamp\":\"2025-03-12T13:34:04.407568Z\",\"rule\":{\"description\":\"Asset `203.0.113.11` created\",\"uuid\":\"00000000-0000-0000-0000-000000000001\",\"name\":\"Unknown Device in the Network\",\"version\":\"1\",\"author\":\"Seckiot\"},\"@version\":\"1\"}\n",
    "event": {
        "category": [
            "host"
        ],
        "ingested": "2025-03-12T13:34:04.407568Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:04.407568Z",
    "host": {
        "id": [
            "11111111-1111-4111-8111-000000000024"
        ],
        "name": [
            "device01.example.com"
        ]
    },
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "Seckiot",
        "description": "Asset `203.0.113.11` created",
        "id": "00000000-0000-0000-0000-000000000001",
        "name": "Unknown Device in the Network",
        "uuid": "00000000-0000-0000-0000-000000000001",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000016"
        },
        "assets": {
            "id": [
                "11111111-1111-4111-8111-000000000024"
            ],
            "name": [
                "device01.example.com"
            ]
        },
        "module": "Cartography"
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T09:29:10.485097Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T09:29:10.485097Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"ip\":\"198.51.100.82\",\"port\":443},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"br0\",\"assets\":[{\"name\":\"device02.example.com\",\"first_seen\":\"2025-03-12T09:28:40Z\",\"last_seen\":\"2025-03-12T09:29:09.346448Z\",\"id\":\"11111111-1111-4111-8111-000000000022\"},{\"system\":\"Windows 2016+ Server\",\"first_seen\":\"2025-03-05T12:37:53.554365Z\",\"last_seen\":\"2025-03-12T09:29:07.350067Z\",\"name\":\"wks01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"version\":\"10.0.10011.16384\",\"primary_ip\":\"11111111-1111-4111-8111-000000000007\",\"id\":\"11111111-1111-4111-8111-000000000009\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"default\",\"session\":\"00000000000000000000000000000001\",\"alert_id\":\"11111111-1111-4111-8111-000000000017\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T09:29:10.485097Z\",\"network\":{\"protocol\":\"TLS\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":50335,\"ip\":\"192.0.2.50\",\"mac\":\"02:00:00:00:00:03\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"New link detected between WKS01 and 198.51.100.82\",\"uuid\":\"00000000-0000-0000-0000-000000000012\",\"name\":\"New Link Between Two Assets\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "network"
        ],
        "ingested": "2025-03-12T09:29:10.485097Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T09:29:10.485097Z",
    "destination": {
        "address": "198.51.100.82",
        "ip": "198.51.100.82",
        "port": 443
    },
    "device": {
        "manufacturer": [
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-111-gi0-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000009",
            "11111111-1111-4111-8111-000000000022"
        ],
        "name": [
            "device02.example.com",
            "wks01.example.com"
        ],
        "os": {
            "name": [
                "Windows 2016+ Server"
            ],
            "version": [
                "10.0.10011.16384"
            ]
        },
        "type": [
            "virtual-server"
        ]
    },
    "network": {
        "protocol": "tls"
    },
    "observer": {
        "ingress": {
            "interface": {
                "name": "br0"
            },
            "zone": "default"
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.50",
            "198.51.100.82"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "New link detected between WKS01 and 198.51.100.82",
        "id": "00000000-0000-0000-0000-000000000012",
        "name": "New Link Between Two Assets",
        "uuid": "00000000-0000-0000-0000-000000000012",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000017"
        },
        "assets": {
            "category": [
                "IT"
            ],
            "entity": [
                "virtual-server"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000009",
                "11111111-1111-4111-8111-000000000022"
            ],
            "localisation": [
                "lab-192-0-2-111-gi0-1.example.org"
            ],
            "name": [
                "device02.example.com",
                "wks01.example.com"
            ],
            "perdue_level": [
                "3"
            ],
            "purdue_level": [
                3
            ],
            "system": [
                "Windows 2016+ Server"
            ],
            "version": [
                "10.0.10011.16384"
            ]
        },
        "catch_area": {
            "name": "default"
        },
        "module": "Cartography",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000001"
        },
        "sniffer": {
            "name": "br0"
        }
    },
    "source": {
        "address": "192.0.2.50",
        "ip": "192.0.2.50",
        "mac": "02:00:00:00:00:03",
        "port": 50335
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-12T13:34:06.487415Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T13:34:06.487415Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"ip\":\"203.0.113.11\",\"port\":443},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"br0\",\"assets\":[{\"name\":\"device01.example.com\",\"first_seen\":\"2025-03-12T13:33:48Z\",\"last_seen\":\"2025-03-12T13:34:04.348385Z\",\"id\":\"11111111-1111-4111-8111-000000000024\"}],\"capture_zone\":\"default\",\"session\":\"00000000000000000000000000000004\",\"alert_id\":\"11111111-1111-4111-8111-000000000023\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T13:34:06.487415Z\",\"network\":{\"protocol\":\"TLS\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":50569,\"ip\":\"203.0.113.1\",\"mac\":\"02:00:00:00:00:01\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"New server port 203.0.113.11:443 (default) detected on 203.0.113.11\",\"uuid\":\"00000000-0000-0000-0000-000000000002\",\"name\":\"New Open Server Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "network"
        ],
        "ingested": "2025-03-12T13:34:06.487415Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:06.487415Z",
    "destination": {
        "address": "203.0.113.11",
        "ip": "203.0.113.11",
        "port": 443
    },
    "host": {
        "id": [
            "11111111-1111-4111-8111-000000000024"
        ],
        "name": [
            "device01.example.com"
        ]
    },
    "network": {
        "protocol": "tls"
    },
    "observer": {
        "ingress": {
            "interface": {
                "name": "br0"
            },
            "zone": "default"
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "203.0.113.1",
            "203.0.113.11"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "New server port 203.0.113.11:443 (default) detected on 203.0.113.11",
        "id": "00000000-0000-0000-0000-000000000002",
        "name": "New Open Server Port",
        "uuid": "00000000-0000-0000-0000-000000000002",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000023"
        },
        "assets": {
            "id": [
                "11111111-1111-4111-8111-000000000024"
            ],
            "name": [
                "device01.example.com"
            ]
        },
        "catch_area": {
            "name": "default"
        },
        "module": "Cartography",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000004"
        },
        "sniffer": {
            "name": "br0"
        }
    },
    "source": {
        "address": "203.0.113.1",
        "ip": "203.0.113.1",
        "mac": "02:00:00:00:00:01",
        "port": 50569
    }
}
{
    "message": "{\"device\": [], \"event\": {\"code\": [], \"severity\": 7, \"outcome\": \"unknown\", \"created\": \"2025-03-12T13:34:04.407568Z\", \"category\": [\"info\"], \"ingested\": \"2025-03-12T13:34:04.407568Z\", \"kind\": \"alert\", \"type\": [\"info\"]}, \"forwarders\": [\"fw_sekoiaIO\"], \"observer\": {\"name\": \"\", \"vendor\": \"Seckiot\", \"product\": \"Seckiot Citadelle\", \"_type\": \"NIDS\", \"version\": \"\"}, \"skt\": {\"module\": \"Cartography\", \"sniffer\": \"\", \"assets\": [], \"capture_zone\": \"\", \"alert_id\": \"11111111-1111-4111-8111-000000000016\", \"sensor\": \"\"}, \"@timestamp\": \"2025-03-12T13:34:04.407568Z\", \"rule\": {\"description\": \"Asset `203.0.113.11` created\", \"uuid\": \"00000000-0000-0000-0000-000000000001\", \"name\": \"Unknown Device in the Network\", \"version\": \"1\", \"author\": \"Seckiot\"}, \"@version\": \"1\"}",
    "event": {
        "category": [
            "host"
        ],
        "ingested": "2025-03-12T13:34:04.407568Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:04.407568Z",
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "Seckiot",
        "description": "Asset `203.0.113.11` created",
        "id": "00000000-0000-0000-0000-000000000001",
        "name": "Unknown Device in the Network",
        "uuid": "00000000-0000-0000-0000-000000000001",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000016"
        },
        "module": "Cartography"
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-06T14:05:57.457022Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-06T14:05:57.457022Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"skt\":{\"module\":\"CVE\",\"sniffer\":\"\",\"assets\":[{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-06T13:49:56.593575Z\",\"last_seen\":\"2025-03-06T14:05:55.420426Z\",\"name\":\"dc01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.379\",\"primary_ip\":\"11111111-1111-4111-8111-000000000013\",\"id\":\"11111111-1111-4111-8111-000000000002\",\"entity\":\"domain-controller\",\"description\":\"DC 1\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"\",\"alert_id\":\"11111111-1111-4111-8111-000000000021\",\"sensor\":\"\"},\"vulnerability\":{\"severity\":\"medium\",\"scanner\":{\"vendor\":\"Seckiot\"},\"reference\":\"http://example.org/exploits/26528/,http://example.org/exploits/26528/\",\"enumeration\":\"CVE\",\"id\":\"CVE-2013-1414\",\"description\":\"New vulnerability CVE-2013-1414 detected on DC01\",\"score\":{\"base\":\"5.1\",\"version\":\"3.1\"},\"category\":null,\"classification\":\"CVSS\"},\"@timestamp\":\"2025-03-06T14:05:57.457022Z\",\"rule\":{\"description\":\"New vulnerability CVE-2013-1414 detected on DC01\",\"uuid\":\"00000000-0000-0000-0000-000000000003\",\"name\":\"Nouvelle Vuln\u00e9rabilit\u00e9 D\u00e9couverte\",\"version\":\"1\",\"author\":\"seckiot\"},\"@version\":\"1\"}\n",
    "event": {
        "category": [
            "vulnerability"
        ],
        "ingested": "2025-03-06T14:05:57.457022Z",
        "kind": "alert",
        "provider": "CVE",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-06T14:05:57.457022Z",
    "device": {
        "manufacturer": [
            "VMware, Inc."
        ],
        "model": {
            "identifier": [
                "VMware7,1"
            ]
        }
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-111-gi0-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000002"
        ],
        "name": [
            "dc01.example.com"
        ],
        "os": {
            "name": [
                "Windows Server 2019 Standard"
            ],
            "version": [
                "17763.379"
            ]
        },
        "type": [
            "domain-controller"
        ]
    },
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "seckiot",
        "description": "New vulnerability CVE-2013-1414 detected on DC01",
        "id": "00000000-0000-0000-0000-000000000003",
        "name": "Nouvelle Vuln\u00e9rabilit\u00e9 D\u00e9couverte",
        "uuid": "00000000-0000-0000-0000-000000000003",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000021"
        },
        "assets": {
            "category": [
                "IT"
            ],
            "description": [
                "DC 1"
            ],
            "entity": [
                "domain-controller"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000002"
            ],
            "localisation": [
                "lab-192-0-2-111-gi0-1.example.org"
            ],
            "name": [
                "dc01.example.com"
            ],
            "perdue_level": [
                "3"
            ],
            "purdue_level": [
                3
            ],
            "system": [
                "Windows Server 2019 Standard"
            ],
            "version": [
                "17763.379"
            ]
        },
        "module": "CVE"
    },
    "vulnerability": {
        "classification": "CVSS",
        "description": "New vulnerability CVE-2013-1414 detected on DC01",
        "enumeration": "CVE",
        "id": "CVE-2013-1414",
        "reference": "http://example.org/exploits/26528/,http://example.org/exploits/26528/",
        "scanner": {
            "vendor": "Seckiot"
        },
        "score": {
            "base": 5.1,
            "version": "3.1"
        },
        "severity": "medium"
    }
}
Extracted Fields
The following table lists the fields that are extracted, normalized under the ECS format, analyzed and indexed by the parser. It should be noted that infered fields are not listed.
| Name | Type | Description |
|---|---|---|
@timestamp |
date |
Date/time when the event originated. |
destination.ip |
ip |
IP address of the destination. |
destination.mac |
keyword |
MAC address of the destination. |
destination.port |
long |
Port of the destination. |
event.ingested |
date |
Timestamp when an event arrived in the central data store. |
event.kind |
keyword |
The kind of the event. The highest categorization field in the hierarchy. |
event.outcome |
keyword |
The outcome of the event. The lowest level categorization field in the hierarchy. |
event.provider |
keyword |
Source of the event. |
event.severity |
long |
Numeric severity of the event. |
event.type |
keyword |
Event type. The third categorization field in the hierarchy. |
host.geo.name |
keyword |
User-defined description of a location. |
host.id |
keyword |
Unique host id. |
host.name |
keyword |
Name of the host. |
host.os.name |
keyword |
Operating system name, without the version. |
host.os.version |
keyword |
Operating system version as a raw string. |
host.type |
keyword |
Type of host. |
network.protocol |
keyword |
Application protocol name. |
network.transport |
keyword |
Protocol Name corresponding to the field iana_number. |
observer.ingress.interface.id |
keyword |
Interface ID |
observer.ingress.interface.name |
keyword |
Interface name |
observer.ingress.zone |
keyword |
Observer ingress zone |
observer.name |
keyword |
Custom name of the observer. |
observer.product |
keyword |
The product name of the observer. |
observer.type |
keyword |
The type of the observer the data is coming from. |
observer.vendor |
keyword |
Vendor name of the observer. |
observer.version |
keyword |
Observer version. |
rule.author |
keyword |
Rule author |
rule.description |
keyword |
Rule description |
rule.id |
keyword |
Rule ID |
rule.name |
keyword |
Rule name |
rule.uuid |
keyword |
Rule UUID |
rule.version |
keyword |
Rule version |
seckiot.alert.id |
keyword |
Unique ID of the alert |
seckiot.assets.category |
keyword |
Category of the assets involved in the alert (IT/OT/IOT) |
seckiot.assets.description |
keyword |
Description of the assets involved in the alert |
seckiot.assets.entity |
text |
(deprecated) use host.type - Entity of the assets involved in the alert |
seckiot.assets.id |
text |
(deprecated) use host.id - Unique ID of the assets involved in the alert |
seckiot.assets.localisation |
text |
(deprecated) use host.geo.name - Localisation of the assets involved in the alert |
seckiot.assets.name |
text |
(deprecated) use host.name - Name of the assets involved in the alert |
seckiot.assets.perdue_level |
text |
(deprecated) use seckiot.assets.purdue_level - Purdue level (0 to 6) of the assets involved in the alert |
seckiot.assets.purdue_level |
long |
Purdue level (0 to 6) of the assets involved in the alert |
seckiot.assets.system |
text |
(deprecated) use host.os.name - Operating system name of the assets involved in the alert |
seckiot.assets.version |
text |
(deprecated) use host.os.version - Operating system version of the assets involved in the alert |
seckiot.capture_zone.id |
keyword |
Identifier (UUID) of the capture zone where the traffic was observed |
seckiot.catch_area.name |
text |
(deprecated) use observer.ingress.zone or seckiot.capture_zone.id - Name or UUID of the capture zone where the traffic was observed |
seckiot.module |
text |
(deprecated) use event.provider - Seckiot module that raised the alert |
seckiot.sensor.name |
text |
(deprecated) use observer.name - Name of the sensor that captured the traffic |
seckiot.session.id |
keyword |
Identifier of the network session that triggered the alert |
seckiot.sniffer.name |
text |
(deprecated) use observer.ingress.interface.name or observer.ingress.interface.id - Name or UUID of the sniffer that captured the traffic |
source.ip |
ip |
IP address of the source. |
source.mac |
keyword |
MAC address of the source. |
source.port |
long |
Port of the source. |
vulnerability.category |
keyword |
Category of a vulnerability. |
vulnerability.classification |
keyword |
Classification of the vulnerability. |
vulnerability.description |
keyword |
Description of the vulnerability. |
vulnerability.enumeration |
keyword |
Identifier of the vulnerability. |
vulnerability.id |
keyword |
ID of the vulnerability. |
vulnerability.reference |
keyword |
Reference of the vulnerability. |
vulnerability.report_id |
keyword |
Scan identification number. |
vulnerability.scanner.vendor |
keyword |
Name of the scanner vendor. |
vulnerability.score.base |
float |
Vulnerability Base score. |
vulnerability.score.environmental |
float |
Vulnerability Environmental score. |
vulnerability.score.temporal |
float |
Vulnerability Temporal score. |
vulnerability.score.version |
keyword |
CVSS version. |
vulnerability.severity |
keyword |
Severity of the vulnerability. |
For more information on the Intake Format, please find the code of the Parser, Smart Descriptions, and Supported Events here.
Detection section
The following section provides information for those who wish to learn more about the detection capabilities enabled by collecting this intake. It includes details about the built-in rule catalog, event categories, and ECS fields extracted from raw events. This is essential for users aiming to create custom detection rules, perform hunting activities, or pivot in the events page.
Related Built-in Rules
The following Sekoia.io built-in rules match the intake Seckiot Citadelle. This documentation is updated automatically and is based solely on the fields used by the intake which are checked against our rules. This means that some rules will be listed but might not be relevant with the intake.
SEKOIA.IO x Seckiot Citadelle on ATT&CK Navigator
Cryptomining
Detection of domain names potentially related to cryptomining activities.
- Effort: master
Dynamic DNS Contacted
Detect communication with dynamic dns domain. This kind of domain is often used by attackers. This rule can trigger false positive in non-controlled environment because dynamic dns is not always malicious.
- Effort: master
Exfiltration Domain
Detects traffic toward a domain flagged as a possible exfiltration vector.
- Effort: master
Remote Access Tool Domain
Detects traffic toward a domain flagged as a Remote Administration Tool (RAT).
- Effort: master
Remote Monitoring and Management Software - AnyDesk
Detect artifacts related to the installation or execution of the Remote Monitoring and Management tool AnyDesk.
- Effort: master
SEKOIA.IO Intelligence Feed
Detect threats based on indicators of compromise (IOCs) collected by SEKOIA's Threat and Detection Research team.
- Effort: elementary
Sekoia.io EICAR Detection
Detects observables in Sekoia.io CTI tagged as EICAR, which are fake samples meant to test detection.
- Effort: master
TOR Usage
Detects TOR usage, based on the IP address and the destination port (filtered on NTP). TOR is short for The Onion Router, and it gets its name from how it works. TOR intercepts the network traffic from one or more apps on user’s computer, usually the user web browser, and shuffles it through a number of randomly-chosen computers before passing it on to its destination. This disguises user location, and makes it harder for servers to pick him/her out on repeat visits, or to tie together separate visits to different sites, this making tracking and surveillance more difficult. Before a network packet starts its journey, user’s computer chooses a random list of relays and repeatedly encrypts the data in multiple layers, like an onion. Each relay knows only enough to strip off the outermost layer of encryption, before passing what’s left on to the next relay in the list.
- Effort: master
TOR Usage Generic Rule
Detects TOR usage globally, whether the IP is a destination or source. TOR is short for The Onion Router, and it gets its name from how it works. TOR intercepts the network traffic from one or more apps on user’s computer, usually the user web browser, and shuffles it through a number of randomly-chosen computers before passing it on to its destination. This disguises user location, and makes it harder for servers to pick him/her out on repeat visits, or to tie together separate visits to different sites, this making tracking and surveillance more difficult. Before a network packet starts its journey, user’s computer chooses a random list of relays and repeatedly encrypts the data in multiple layers, like an onion. Each relay knows only enough to strip off the outermost layer of encryption, before passing what’s left on to the next relay in the list.
- Effort: master
Event Categories
The following table lists the data source offered by this integration.
| Data Source | Description |
|---|---|
Network intrusion detection system |
Seckiot Citadelle identify suspicious behaviors by providing alerts logs |
Network device logs |
The logs provided by Seckiot Citadelle give a good overview of the network activity |
Network protocol analysis |
The logs offered by Seckiot Citadelle provide traffic analysis |
Asset Management |
Seckiot Citadelle identify all devices and provide a complete visibility |
Transformed Events Samples after Ingestion
This section demonstrates how the raw logs will be transformed by our parsers. It shows the extracted fields that will be available for use in the built-in detection rules and hunting activities in the events page. Understanding these transformations is essential for analysts to create effective detection mechanisms with custom detection rules and to leverage the full potential of the collected data.
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T08:51:28.586238Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T08:51:28.586238Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"Fortinet, Inc.\",\"port\":58629,\"ip\":\"192.0.2.100\",\"mac\":\"02:00:00:00:00:05\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"first_seen\":\"2025-03-05T12:37:56.174487Z\",\"last_seen\":\"2025-03-12T08:50:59.469469Z\",\"name\":\"fw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"LANNER ELECTRONICS, INC.\",\"level\":\"2\",\"primary_ip\":\"11111111-1111-4111-8111-000000000011\",\"id\":\"11111111-1111-4111-8111-000000000014\",\"entity\":\"router\",\"description\":\"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T08:51:00.348Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000002\",\"alert_id\":\"11111111-1111-4111-8111-000000000003\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T08:51:28.586238Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"dns\"},\"@version\":\"1\",\"source\":{\"vendor\":\"LANNER ELECTRONICS, INC.\",\"port\":53,\"ip\":\"203.0.113.254\",\"mac\":\"02:00:00:00:00:04\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\",\"uuid\":\"51186749-7415-46be-90e5-000000000080\",\"name\":\"Network Service Discovery - UDP Scan Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "2",
                "3"
            ],
            "purdue_level": [
                2,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\": [], \"event\": {\"code\": [], \"severity\": 1, \"outcome\": \"unknown\", \"created\": \"2025-03-12T08:51:28.586238Z\", \"category\": [\"info\"], \"ingested\": \"2025-03-12T08:51:28.586238Z\", \"kind\": \"alert\", \"type\": [\"info\"]}, \"forwarders\": [\"fw_sekoiaIO\"], \"destination\": {\"vendor\": \"Fortinet, Inc.\", \"port\": 58629, \"ip\": \"192.0.2.100\", \"mac\": \"02:00:00:00:00:05\"}, \"skt\": {\"module\": \"Other\", \"sniffer\": \"11111111-1111-4111-8111-000000000010\", \"assets\": [{\"first_seen\": \"2025-03-05T12:37:56.174487Z\", \"last_seen\": \"2025-03-12T08:50:59.469469Z\", \"name\": \"fw01.example.com\", \"category\": \"IT\", \"hardware_vendor\": \"LANNER ELECTRONICS, INC.\", \"level\": 0, \"primary_ip\": \"11111111-1111-4111-8111-000000000011\", \"id\": \"11111111-1111-4111-8111-000000000014\", \"entity\": \"router\", \"description\": \"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\", \"localisation\": \"lab-192-0-2-101-ge-1-26.example.org\"}, {\"system\": \"Windows\", \"first_seen\": \"2025-03-05T12:37:56.077529Z\", \"last_seen\": \"2025-03-12T08:51:00.348Z\", \"name\": \"gw01.example.com\", \"category\": \"IT\", \"hardware_vendor\": \"VMware, Inc.\", \"level\": 3, \"primary_ip\": \"11111111-1111-4111-8111-000000000004\", \"id\": \"11111111-1111-4111-8111-000000000012\", \"entity\": \"router\", \"localisation\": \"lab-192-0-2-121-1-2-1.example.org\"}], \"capture_zone\": \"11111111-1111-4111-8111-000000000018\", \"session\": \"00000000000000000000000000000002\", \"alert_id\": \"11111111-1111-4111-8111-000000000003\", \"sensor\": \"SENSOR-0\"}, \"@timestamp\": \"2025-03-12T08:51:28.586238Z\", \"network\": {\"transport\": \"UDP\", \"protocol\": \"dns\"}, \"@version\": \"1\", \"source\": {\"vendor\": \"LANNER ELECTRONICS, INC.\", \"port\": 53, \"ip\": \"203.0.113.254\", \"mac\": \"02:00:00:00:00:04\"}, \"observer\": {\"name\": \"citadelle-01\", \"vendor\": \"Seckiot\", \"product\": \"Seckiot Citadelle\", \"_type\": \"NIDS\", \"version\": \"\"}, \"rule\": {\"description\": \"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\", \"uuid\": \"51186749-7415-46be-90e5-000000000080\", \"name\": \"Network Service Discovery - UDP Scan Port\", \"version\": \"1\", \"author\": \"Seckiot\"}}",
    "event": {
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Other",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "citadelle-01",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "0",
                "3"
            ],
            "purdue_level": [
                0,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Other",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T08:51:28.586238Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T08:51:28.586238Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"Fortinet, Inc.\",\"port\":58629,\"ip\":\"192.0.2.100\",\"mac\":\"02:00:00:00:00:05\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"first_seen\":\"2025-03-05T12:37:56.174487Z\",\"last_seen\":\"2025-03-12T08:50:59.469469Z\",\"name\":\"fw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"LANNER ELECTRONICS, INC.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000011\",\"id\":\"11111111-1111-4111-8111-000000000014\",\"entity\":\"router\",\"description\":\"pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T08:51:00.348Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000002\",\"alert_id\":\"11111111-1111-4111-8111-000000000003\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T08:51:28.586238Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"dns\"},\"@version\":\"1\",\"source\":{\"vendor\":\"LANNER ELECTRONICS, INC.\",\"port\":53,\"ip\":\"203.0.113.254\",\"mac\":\"02:00:00:00:00:04\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.\",\"uuid\":\"51186749-7415-46be-90e5-000000000080\",\"name\":\"Network Service Discovery - UDP Scan Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T08:51:28.586238Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T08:51:28.586238Z",
    "destination": {
        "address": "192.0.2.100",
        "ip": "192.0.2.100",
        "mac": "02:00:00:00:00:05",
        "port": 58629
    },
    "device": {
        "manufacturer": [
            "LANNER ELECTRONICS, INC.",
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000014"
        ],
        "name": [
            "fw01.example.com",
            "gw01.example.com"
        ],
        "os": {
            "name": [
                "Windows"
            ]
        },
        "type": [
            "router",
            "router"
        ]
    },
    "network": {
        "protocol": "dns",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.100",
            "203.0.113.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "Large number of requests sent from the same machine to the same machine on different ports using only a UDP packet to see if the port is open or closed. This is typically used by the tool NMAP.",
        "id": "51186749-7415-46be-90e5-000000000080",
        "name": "Network Service Discovery - UDP Scan Port",
        "uuid": "51186749-7415-46be-90e5-000000000080",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000003"
        },
        "assets": {
            "category": [
                "IT",
                "IT"
            ],
            "description": [
                "pfSense fw01.example.com 2.7.0-RELEASE FreeBSD 14.0-CURRENT amd64"
            ],
            "entity": [
                "router",
                "router"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000014"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "fw01.example.com",
                "gw01.example.com"
            ],
            "perdue_level": [
                "3",
                "3"
            ],
            "purdue_level": [
                3,
                3
            ],
            "system": [
                "Windows"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000002"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "203.0.113.254",
        "ip": "203.0.113.254",
        "mac": "02:00:00:00:00:04",
        "port": 53
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T07:31:28.525356Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T07:31:28.525356Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"vendor\":\"VMware, Inc.\",\"port\":4739,\"ip\":\"198.51.100.1\",\"mac\":\"02:00:00:00:00:02\"},\"skt\":{\"module\":\"Detection Engine\",\"sniffer\":\"11111111-1111-4111-8111-000000000010\",\"assets\":[{\"system\":\"Windows\",\"first_seen\":\"2025-03-05T12:37:56.077529Z\",\"last_seen\":\"2025-03-12T07:31:12.375646Z\",\"name\":\"gw01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000004\",\"id\":\"11111111-1111-4111-8111-000000000012\",\"entity\":\"router\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"first_seen\":\"2025-03-06T13:57:58.838858Z\",\"last_seen\":\"2025-03-12T07:30:53.844522Z\",\"name\":\"fw02.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"Fortinet, Inc.\",\"level\":3,\"primary_ip\":\"11111111-1111-4111-8111-000000000020\",\"id\":\"11111111-1111-4111-8111-000000000001\",\"entity\":\"router\",\"description\":\"Firewall Site 2\",\"localisation\":\"lab-192-0-2-101-ge-1-26.example.org\"},{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-05T12:37:53.554365Z\",\"last_seen\":\"2025-03-12T07:31:11.928426Z\",\"name\":\"srv02.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.4737\",\"primary_ip\":\"11111111-1111-4111-8111-000000000006\",\"id\":\"11111111-1111-4111-8111-000000000019\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"system\":\"Windows 2016+ Server\",\"first_seen\":\"2025-03-06T13:57:57.628789Z\",\"last_seen\":\"2025-03-12T07:31:21.084186Z\",\"name\":\"srv01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"version\":\"10.0.10011.16384\",\"primary_ip\":\"11111111-1111-4111-8111-000000000008\",\"id\":\"11111111-1111-4111-8111-000000000005\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-121-1-2-1.example.org\"},{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-06T13:49:56.593575Z\",\"last_seen\":\"2025-03-12T07:31:12.347024Z\",\"name\":\"dc01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.379\",\"primary_ip\":\"11111111-1111-4111-8111-000000000013\",\"id\":\"11111111-1111-4111-8111-000000000002\",\"entity\":\"domain-controller\",\"description\":\"DC 1\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"11111111-1111-4111-8111-000000000018\",\"session\":\"00000000000000000000000000000003\",\"alert_id\":\"11111111-1111-4111-8111-000000000015\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T07:31:28.525356Z\",\"network\":{\"transport\":\"UDP\",\"protocol\":\"iana_ipfix\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":8346,\"ip\":\"198.51.100.254\",\"mac\":\"02:00:00:00:00:01\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"A UDP flood Denial of Service attack involves sending a large number of UDP packets to random ports on a target. This overloads the target's network and resources, leading to performance degradation or unavailability of the service to legitimate users.\",\"uuid\":\"51186749-7415-46be-90e5-000000000087\",\"name\":\"Denial Of Service - UDP Flood\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "intrusion_detection"
        ],
        "ingested": "2025-03-12T07:31:28.525356Z",
        "kind": "alert",
        "provider": "Detection Engine",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T07:31:28.525356Z",
    "destination": {
        "address": "198.51.100.1",
        "ip": "198.51.100.1",
        "mac": "02:00:00:00:00:02",
        "port": 4739
    },
    "device": {
        "manufacturer": [
            "Fortinet, Inc.",
            "VMware, Inc.",
            "VMware, Inc.",
            "VMware, Inc.",
            "VMware, Inc."
        ],
        "model": {
            "identifier": [
                "VMware7,1",
                "VMware7,1"
            ]
        }
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-111-gi0-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000001",
            "11111111-1111-4111-8111-000000000002",
            "11111111-1111-4111-8111-000000000005",
            "11111111-1111-4111-8111-000000000012",
            "11111111-1111-4111-8111-000000000019"
        ],
        "name": [
            "dc01.example.com",
            "fw02.example.com",
            "gw01.example.com",
            "srv01.example.com",
            "srv02.example.com"
        ],
        "os": {
            "name": [
                "Windows",
                "Windows 2016+ Server",
                "Windows Server 2019 Standard",
                "Windows Server 2019 Standard"
            ],
            "version": [
                "10.0.10011.16384",
                "17763.379",
                "17763.4737"
            ]
        },
        "type": [
            "domain-controller",
            "router",
            "router",
            "virtual-server",
            "virtual-server"
        ]
    },
    "network": {
        "protocol": "iana_ipfix",
        "transport": "udp"
    },
    "observer": {
        "ingress": {
            "interface": {
                "id": "11111111-1111-4111-8111-000000000010"
            }
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "198.51.100.1",
            "198.51.100.254"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "A UDP flood Denial of Service attack involves sending a large number of UDP packets to random ports on a target. This overloads the target's network and resources, leading to performance degradation or unavailability of the service to legitimate users.",
        "id": "51186749-7415-46be-90e5-000000000087",
        "name": "Denial Of Service - UDP Flood",
        "uuid": "51186749-7415-46be-90e5-000000000087",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000015"
        },
        "assets": {
            "category": [
                "IT",
                "IT",
                "IT",
                "IT",
                "IT"
            ],
            "description": [
                "DC 1",
                "Firewall Site 2"
            ],
            "entity": [
                "domain-controller",
                "router",
                "router",
                "virtual-server",
                "virtual-server"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000001",
                "11111111-1111-4111-8111-000000000002",
                "11111111-1111-4111-8111-000000000005",
                "11111111-1111-4111-8111-000000000012",
                "11111111-1111-4111-8111-000000000019"
            ],
            "localisation": [
                "lab-192-0-2-101-ge-1-26.example.org",
                "lab-192-0-2-111-gi0-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org",
                "lab-192-0-2-121-1-2-1.example.org"
            ],
            "name": [
                "dc01.example.com",
                "fw02.example.com",
                "gw01.example.com",
                "srv01.example.com",
                "srv02.example.com"
            ],
            "perdue_level": [
                "3",
                "3",
                "3",
                "3",
                "3"
            ],
            "purdue_level": [
                3,
                3,
                3,
                3,
                3
            ],
            "system": [
                "Windows",
                "Windows 2016+ Server",
                "Windows Server 2019 Standard",
                "Windows Server 2019 Standard"
            ],
            "version": [
                "10.0.10011.16384",
                "17763.379",
                "17763.4737"
            ]
        },
        "capture_zone": {
            "id": "11111111-1111-4111-8111-000000000018"
        },
        "catch_area": {
            "name": "11111111-1111-4111-8111-000000000018"
        },
        "module": "Detection Engine",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000003"
        },
        "sniffer": {
            "name": "11111111-1111-4111-8111-000000000010"
        }
    },
    "source": {
        "address": "198.51.100.254",
        "ip": "198.51.100.254",
        "mac": "02:00:00:00:00:01",
        "port": 8346
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-12T13:34:04.407568Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T13:34:04.407568Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"\",\"assets\":[{\"name\":\"device01.example.com\",\"first_seen\":\"2025-03-12T13:33:48Z\",\"last_seen\":\"2025-03-12T13:34:04.348385Z\",\"id\":\"11111111-1111-4111-8111-000000000024\"}],\"capture_zone\":\"\",\"alert_id\":\"11111111-1111-4111-8111-000000000016\",\"sensor\":\"\"},\"@timestamp\":\"2025-03-12T13:34:04.407568Z\",\"rule\":{\"description\":\"Asset `203.0.113.11` created\",\"uuid\":\"00000000-0000-0000-0000-000000000001\",\"name\":\"Unknown Device in the Network\",\"version\":\"1\",\"author\":\"Seckiot\"},\"@version\":\"1\"}\n",
    "event": {
        "category": [
            "host"
        ],
        "ingested": "2025-03-12T13:34:04.407568Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:04.407568Z",
    "host": {
        "id": [
            "11111111-1111-4111-8111-000000000024"
        ],
        "name": [
            "device01.example.com"
        ]
    },
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "Seckiot",
        "description": "Asset `203.0.113.11` created",
        "id": "00000000-0000-0000-0000-000000000001",
        "name": "Unknown Device in the Network",
        "uuid": "00000000-0000-0000-0000-000000000001",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000016"
        },
        "assets": {
            "id": [
                "11111111-1111-4111-8111-000000000024"
            ],
            "name": [
                "device01.example.com"
            ]
        },
        "module": "Cartography"
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":1,\"outcome\":\"unknown\",\"created\":\"2025-03-12T09:29:10.485097Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T09:29:10.485097Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"ip\":\"198.51.100.82\",\"port\":443},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"br0\",\"assets\":[{\"name\":\"device02.example.com\",\"first_seen\":\"2025-03-12T09:28:40Z\",\"last_seen\":\"2025-03-12T09:29:09.346448Z\",\"id\":\"11111111-1111-4111-8111-000000000022\"},{\"system\":\"Windows 2016+ Server\",\"first_seen\":\"2025-03-05T12:37:53.554365Z\",\"last_seen\":\"2025-03-12T09:29:07.350067Z\",\"name\":\"wks01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"level\":3,\"version\":\"10.0.10011.16384\",\"primary_ip\":\"11111111-1111-4111-8111-000000000007\",\"id\":\"11111111-1111-4111-8111-000000000009\",\"entity\":\"virtual-server\",\"description\":\"\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"default\",\"session\":\"00000000000000000000000000000001\",\"alert_id\":\"11111111-1111-4111-8111-000000000017\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T09:29:10.485097Z\",\"network\":{\"protocol\":\"TLS\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":50335,\"ip\":\"192.0.2.50\",\"mac\":\"02:00:00:00:00:03\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"New link detected between WKS01 and 198.51.100.82\",\"uuid\":\"00000000-0000-0000-0000-000000000012\",\"name\":\"New Link Between Two Assets\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "network"
        ],
        "ingested": "2025-03-12T09:29:10.485097Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 1,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T09:29:10.485097Z",
    "destination": {
        "address": "198.51.100.82",
        "ip": "198.51.100.82",
        "port": 443
    },
    "device": {
        "manufacturer": [
            "VMware, Inc."
        ]
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-111-gi0-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000009",
            "11111111-1111-4111-8111-000000000022"
        ],
        "name": [
            "device02.example.com",
            "wks01.example.com"
        ],
        "os": {
            "name": [
                "Windows 2016+ Server"
            ],
            "version": [
                "10.0.10011.16384"
            ]
        },
        "type": [
            "virtual-server"
        ]
    },
    "network": {
        "protocol": "tls"
    },
    "observer": {
        "ingress": {
            "interface": {
                "name": "br0"
            },
            "zone": "default"
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "192.0.2.50",
            "198.51.100.82"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "New link detected between WKS01 and 198.51.100.82",
        "id": "00000000-0000-0000-0000-000000000012",
        "name": "New Link Between Two Assets",
        "uuid": "00000000-0000-0000-0000-000000000012",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000017"
        },
        "assets": {
            "category": [
                "IT"
            ],
            "entity": [
                "virtual-server"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000009",
                "11111111-1111-4111-8111-000000000022"
            ],
            "localisation": [
                "lab-192-0-2-111-gi0-1.example.org"
            ],
            "name": [
                "device02.example.com",
                "wks01.example.com"
            ],
            "perdue_level": [
                "3"
            ],
            "purdue_level": [
                3
            ],
            "system": [
                "Windows 2016+ Server"
            ],
            "version": [
                "10.0.10011.16384"
            ]
        },
        "catch_area": {
            "name": "default"
        },
        "module": "Cartography",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000001"
        },
        "sniffer": {
            "name": "br0"
        }
    },
    "source": {
        "address": "192.0.2.50",
        "ip": "192.0.2.50",
        "mac": "02:00:00:00:00:03",
        "port": 50335
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-12T13:34:06.487415Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-12T13:34:06.487415Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"destination\":{\"ip\":\"203.0.113.11\",\"port\":443},\"skt\":{\"module\":\"Cartography\",\"sniffer\":\"br0\",\"assets\":[{\"name\":\"device01.example.com\",\"first_seen\":\"2025-03-12T13:33:48Z\",\"last_seen\":\"2025-03-12T13:34:04.348385Z\",\"id\":\"11111111-1111-4111-8111-000000000024\"}],\"capture_zone\":\"default\",\"session\":\"00000000000000000000000000000004\",\"alert_id\":\"11111111-1111-4111-8111-000000000023\",\"sensor\":\"SENSOR-0\"},\"@timestamp\":\"2025-03-12T13:34:06.487415Z\",\"network\":{\"protocol\":\"TLS\"},\"@version\":\"1\",\"source\":{\"vendor\":\"VMware, Inc.\",\"port\":50569,\"ip\":\"203.0.113.1\",\"mac\":\"02:00:00:00:00:01\"},\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"rule\":{\"description\":\"New server port 203.0.113.11:443 (default) detected on 203.0.113.11\",\"uuid\":\"00000000-0000-0000-0000-000000000002\",\"name\":\"New Open Server Port\",\"version\":\"1\",\"author\":\"Seckiot\"}}\n",
    "event": {
        "category": [
            "network"
        ],
        "ingested": "2025-03-12T13:34:06.487415Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:06.487415Z",
    "destination": {
        "address": "203.0.113.11",
        "ip": "203.0.113.11",
        "port": 443
    },
    "host": {
        "id": [
            "11111111-1111-4111-8111-000000000024"
        ],
        "name": [
            "device01.example.com"
        ]
    },
    "network": {
        "protocol": "tls"
    },
    "observer": {
        "ingress": {
            "interface": {
                "name": "br0"
            },
            "zone": "default"
        },
        "name": "SENSOR-0",
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "related": {
        "ip": [
            "203.0.113.1",
            "203.0.113.11"
        ]
    },
    "rule": {
        "author": "Seckiot",
        "description": "New server port 203.0.113.11:443 (default) detected on 203.0.113.11",
        "id": "00000000-0000-0000-0000-000000000002",
        "name": "New Open Server Port",
        "uuid": "00000000-0000-0000-0000-000000000002",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000023"
        },
        "assets": {
            "id": [
                "11111111-1111-4111-8111-000000000024"
            ],
            "name": [
                "device01.example.com"
            ]
        },
        "catch_area": {
            "name": "default"
        },
        "module": "Cartography",
        "sensor": {
            "name": "SENSOR-0"
        },
        "session": {
            "id": "00000000000000000000000000000004"
        },
        "sniffer": {
            "name": "br0"
        }
    },
    "source": {
        "address": "203.0.113.1",
        "ip": "203.0.113.1",
        "mac": "02:00:00:00:00:01",
        "port": 50569
    }
}
{
    "message": "{\"device\": [], \"event\": {\"code\": [], \"severity\": 7, \"outcome\": \"unknown\", \"created\": \"2025-03-12T13:34:04.407568Z\", \"category\": [\"info\"], \"ingested\": \"2025-03-12T13:34:04.407568Z\", \"kind\": \"alert\", \"type\": [\"info\"]}, \"forwarders\": [\"fw_sekoiaIO\"], \"observer\": {\"name\": \"\", \"vendor\": \"Seckiot\", \"product\": \"Seckiot Citadelle\", \"_type\": \"NIDS\", \"version\": \"\"}, \"skt\": {\"module\": \"Cartography\", \"sniffer\": \"\", \"assets\": [], \"capture_zone\": \"\", \"alert_id\": \"11111111-1111-4111-8111-000000000016\", \"sensor\": \"\"}, \"@timestamp\": \"2025-03-12T13:34:04.407568Z\", \"rule\": {\"description\": \"Asset `203.0.113.11` created\", \"uuid\": \"00000000-0000-0000-0000-000000000001\", \"name\": \"Unknown Device in the Network\", \"version\": \"1\", \"author\": \"Seckiot\"}, \"@version\": \"1\"}",
    "event": {
        "category": [
            "host"
        ],
        "ingested": "2025-03-12T13:34:04.407568Z",
        "kind": "alert",
        "provider": "Cartography",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-12T13:34:04.407568Z",
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "Seckiot",
        "description": "Asset `203.0.113.11` created",
        "id": "00000000-0000-0000-0000-000000000001",
        "name": "Unknown Device in the Network",
        "uuid": "00000000-0000-0000-0000-000000000001",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000016"
        },
        "module": "Cartography"
    }
}
{
    "message": "{\"device\":[],\"event\":{\"code\":[],\"severity\":7,\"outcome\":\"unknown\",\"created\":\"2025-03-06T14:05:57.457022Z\",\"category\":[\"info\"],\"ingested\":\"2025-03-06T14:05:57.457022Z\",\"kind\":\"alert\",\"type\":[\"info\"]},\"forwarders\":[\"fw_sekoiaIO\"],\"observer\":{\"name\":\"\",\"vendor\":\"Seckiot\",\"product\":\"Seckiot Citadelle\",\"_type\":\"NIDS\",\"version\":\"\"},\"skt\":{\"module\":\"CVE\",\"sniffer\":\"\",\"assets\":[{\"system\":\"Windows Server 2019 Standard\",\"first_seen\":\"2025-03-06T13:49:56.593575Z\",\"last_seen\":\"2025-03-06T14:05:55.420426Z\",\"name\":\"dc01.example.com\",\"category\":\"IT\",\"hardware_vendor\":\"VMware, Inc.\",\"modele\":\"VMware7,1\",\"level\":3,\"version\":\"17763.379\",\"primary_ip\":\"11111111-1111-4111-8111-000000000013\",\"id\":\"11111111-1111-4111-8111-000000000002\",\"entity\":\"domain-controller\",\"description\":\"DC 1\",\"localisation\":\"lab-192-0-2-111-gi0-1.example.org\"}],\"capture_zone\":\"\",\"alert_id\":\"11111111-1111-4111-8111-000000000021\",\"sensor\":\"\"},\"vulnerability\":{\"severity\":\"medium\",\"scanner\":{\"vendor\":\"Seckiot\"},\"reference\":\"http://example.org/exploits/26528/,http://example.org/exploits/26528/\",\"enumeration\":\"CVE\",\"id\":\"CVE-2013-1414\",\"description\":\"New vulnerability CVE-2013-1414 detected on DC01\",\"score\":{\"base\":\"5.1\",\"version\":\"3.1\"},\"category\":null,\"classification\":\"CVSS\"},\"@timestamp\":\"2025-03-06T14:05:57.457022Z\",\"rule\":{\"description\":\"New vulnerability CVE-2013-1414 detected on DC01\",\"uuid\":\"00000000-0000-0000-0000-000000000003\",\"name\":\"Nouvelle Vuln\u00e9rabilit\u00e9 D\u00e9couverte\",\"version\":\"1\",\"author\":\"seckiot\"},\"@version\":\"1\"}\n",
    "event": {
        "category": [
            "vulnerability"
        ],
        "ingested": "2025-03-06T14:05:57.457022Z",
        "kind": "alert",
        "provider": "CVE",
        "severity": 7,
        "type": [
            "info"
        ]
    },
    "@timestamp": "2025-03-06T14:05:57.457022Z",
    "device": {
        "manufacturer": [
            "VMware, Inc."
        ],
        "model": {
            "identifier": [
                "VMware7,1"
            ]
        }
    },
    "host": {
        "geo": {
            "name": [
                "lab-192-0-2-111-gi0-1.example.org"
            ]
        },
        "id": [
            "11111111-1111-4111-8111-000000000002"
        ],
        "name": [
            "dc01.example.com"
        ],
        "os": {
            "name": [
                "Windows Server 2019 Standard"
            ],
            "version": [
                "17763.379"
            ]
        },
        "type": [
            "domain-controller"
        ]
    },
    "observer": {
        "product": "Seckiot Citadelle",
        "type": "NIDS",
        "vendor": "Seckiot"
    },
    "rule": {
        "author": "seckiot",
        "description": "New vulnerability CVE-2013-1414 detected on DC01",
        "id": "00000000-0000-0000-0000-000000000003",
        "name": "Nouvelle Vuln\u00e9rabilit\u00e9 D\u00e9couverte",
        "uuid": "00000000-0000-0000-0000-000000000003",
        "version": "1"
    },
    "seckiot": {
        "alert": {
            "id": "11111111-1111-4111-8111-000000000021"
        },
        "assets": {
            "category": [
                "IT"
            ],
            "description": [
                "DC 1"
            ],
            "entity": [
                "domain-controller"
            ],
            "id": [
                "11111111-1111-4111-8111-000000000002"
            ],
            "localisation": [
                "lab-192-0-2-111-gi0-1.example.org"
            ],
            "name": [
                "dc01.example.com"
            ],
            "perdue_level": [
                "3"
            ],
            "purdue_level": [
                3
            ],
            "system": [
                "Windows Server 2019 Standard"
            ],
            "version": [
                "17763.379"
            ]
        },
        "module": "CVE"
    },
    "vulnerability": {
        "classification": "CVSS",
        "description": "New vulnerability CVE-2013-1414 detected on DC01",
        "enumeration": "CVE",
        "id": "CVE-2013-1414",
        "reference": "http://example.org/exploits/26528/,http://example.org/exploits/26528/",
        "scanner": {
            "vendor": "Seckiot"
        },
        "score": {
            "base": 5.1,
            "version": "3.1"
        },
        "severity": "medium"
    }
}
Extracted Fields
The following table lists the fields that are extracted, normalized under the ECS format, analyzed and indexed by the parser. It should be noted that infered fields are not listed.
| Name | Type | Description |
|---|---|---|
@timestamp |
date |
Date/time when the event originated. |
destination.ip |
ip |
IP address of the destination. |
destination.mac |
keyword |
MAC address of the destination. |
destination.port |
long |
Port of the destination. |
event.ingested |
date |
Timestamp when an event arrived in the central data store. |
event.kind |
keyword |
The kind of the event. The highest categorization field in the hierarchy. |
event.outcome |
keyword |
The outcome of the event. The lowest level categorization field in the hierarchy. |
event.provider |
keyword |
Source of the event. |
event.severity |
long |
Numeric severity of the event. |
event.type |
keyword |
Event type. The third categorization field in the hierarchy. |
host.geo.name |
keyword |
User-defined description of a location. |
host.id |
keyword |
Unique host id. |
host.name |
keyword |
Name of the host. |
host.os.name |
keyword |
Operating system name, without the version. |
host.os.version |
keyword |
Operating system version as a raw string. |
host.type |
keyword |
Type of host. |
network.protocol |
keyword |
Application protocol name. |
network.transport |
keyword |
Protocol Name corresponding to the field iana_number. |
observer.ingress.interface.id |
keyword |
Interface ID |
observer.ingress.interface.name |
keyword |
Interface name |
observer.ingress.zone |
keyword |
Observer ingress zone |
observer.name |
keyword |
Custom name of the observer. |
observer.product |
keyword |
The product name of the observer. |
observer.type |
keyword |
The type of the observer the data is coming from. |
observer.vendor |
keyword |
Vendor name of the observer. |
observer.version |
keyword |
Observer version. |
rule.author |
keyword |
Rule author |
rule.description |
keyword |
Rule description |
rule.id |
keyword |
Rule ID |
rule.name |
keyword |
Rule name |
rule.uuid |
keyword |
Rule UUID |
rule.version |
keyword |
Rule version |
seckiot.alert.id |
keyword |
Unique ID of the alert |
seckiot.assets.category |
keyword |
Category of the assets involved in the alert (IT/OT/IOT) |
seckiot.assets.description |
keyword |
Description of the assets involved in the alert |
seckiot.assets.entity |
text |
(deprecated) use host.type - Entity of the assets involved in the alert |
seckiot.assets.id |
text |
(deprecated) use host.id - Unique ID of the assets involved in the alert |
seckiot.assets.localisation |
text |
(deprecated) use host.geo.name - Localisation of the assets involved in the alert |
seckiot.assets.name |
text |
(deprecated) use host.name - Name of the assets involved in the alert |
seckiot.assets.perdue_level |
text |
(deprecated) use seckiot.assets.purdue_level - Purdue level (0 to 6) of the assets involved in the alert |
seckiot.assets.purdue_level |
long |
Purdue level (0 to 6) of the assets involved in the alert |
seckiot.assets.system |
text |
(deprecated) use host.os.name - Operating system name of the assets involved in the alert |
seckiot.assets.version |
text |
(deprecated) use host.os.version - Operating system version of the assets involved in the alert |
seckiot.capture_zone.id |
keyword |
Identifier (UUID) of the capture zone where the traffic was observed |
seckiot.catch_area.name |
text |
(deprecated) use observer.ingress.zone or seckiot.capture_zone.id - Name or UUID of the capture zone where the traffic was observed |
seckiot.module |
text |
(deprecated) use event.provider - Seckiot module that raised the alert |
seckiot.sensor.name |
text |
(deprecated) use observer.name - Name of the sensor that captured the traffic |
seckiot.session.id |
keyword |
Identifier of the network session that triggered the alert |
seckiot.sniffer.name |
text |
(deprecated) use observer.ingress.interface.name or observer.ingress.interface.id - Name or UUID of the sniffer that captured the traffic |
source.ip |
ip |
IP address of the source. |
source.mac |
keyword |
MAC address of the source. |
source.port |
long |
Port of the source. |
vulnerability.category |
keyword |
Category of a vulnerability. |
vulnerability.classification |
keyword |
Classification of the vulnerability. |
vulnerability.description |
keyword |
Description of the vulnerability. |
vulnerability.enumeration |
keyword |
Identifier of the vulnerability. |
vulnerability.id |
keyword |
ID of the vulnerability. |
vulnerability.reference |
keyword |
Reference of the vulnerability. |
vulnerability.report_id |
keyword |
Scan identification number. |
vulnerability.scanner.vendor |
keyword |
Name of the scanner vendor. |
vulnerability.score.base |
float |
Vulnerability Base score. |
vulnerability.score.environmental |
float |
Vulnerability Environmental score. |
vulnerability.score.temporal |
float |
Vulnerability Temporal score. |
vulnerability.score.version |
keyword |
CVSS version. |
vulnerability.severity |
keyword |
Severity of the vulnerability. |
For more information on the Intake Format, please find the code of the Parser, Smart Descriptions, and Supported Events here.